❌

Reading view

Ahold Delhaize Reports Malicious Cyberattack as Supermarket Deliveries Remain Disrupted

Dutch-Belgian supermarket group Ahold Delhaize has confirmed that malicious activity was responsible for the cybersecurity incident that disrupted its operations across Europe and the United States, forcing the company to take websites, applications and other computer systems offline.

In an official statement issued on Monday, 19 October, the company announced that it had filed a formal complaint with Dutch police and was cooperating with national cybersecurity authorities. Although physical supermarkets have remained open, the disruption has affected online shopping, deliveries and some distribution operations.

The company said investigators had so far found no evidence that sensitive information belonging to customers, employees or business partners had been taken. However, its investigation remains open, and the identity and objectives of those responsible have not been publicly established.

Online services interrupted across several countries

The disruption began on 12 October, when Ahold Delhaize detected suspicious activity within its information technology infrastructure.

The group responded by taking a number of systems offline as a precaution, affecting most of its retail brands in Europe and the United States. The consequences varied considerably between businesses, with some experiencing prolonged interruption to digital services while others were able to restore operations more quickly.

Albert Heijn, the Netherlands’ largest supermarket chain, has been particularly affected. Its website and mobile application have returned online, but home grocery deliveries are not expected to resume until Friday, 23 October.

Orders scheduled before that date have been cancelled, while the company continues preparations for a gradual restoration of its online delivery service.

The incident also interrupted some supply and distribution arrangements, resulting in shortages on supermarket shelves in parts of the Netherlands and Belgium.

In Belgium, Delhaize has restored its online shopping operations. Certain promotional and personalised services were still experiencing difficulties, although the parent company confirmed that its Belgian e-commerce business was operational again.

Dutch retailers Etos and Gall & Gall have also restored their websites. Meanwhile, several American supermarket brands owned by Ahold Delhaize have continued to experience service interruptions.

The group said it expected additional online services in the United States to become available over the coming days.

Dutch authorities investigate

Ahold Delhaize said it notified the Netherlands’ National Cyber Security Centre within 24 hours of detecting the malicious activity.

The company has subsequently provided updates to the authorities and, on Monday, confirmed that a formal police report had been submitted.

Chief executive Frans Muller defended the decision to shut down digital systems, arguing that the investigation had demonstrated the necessity of taking preventive action.

The company has not identified the perpetrators, confirmed whether ransomware was involved or disclosed the technical method used to gain access to its infrastructure.

These distinctions are important because malicious activity does not necessarily establish that information was stolen or that attackers obtained control over every system subsequently taken offline.

The retailer has instead described a controlled restoration process intended to ensure that affected systems can be brought back into operation without exposing the business to further risks.

Ahold Delhaize operates thousands of supermarkets and related retail businesses, including Albert Heijn, Delhaize, Food Lion, Giant Food, Hannaford and Stop & Shop.

Its geographical reach means that a disruption originating within shared corporate infrastructure can affect several national markets, even where individual retail chains maintain separate commercial operations.

Cybersecurity becomes a supply-chain concern

The attack comes amid increasing scrutiny of the vulnerability of European food retailers to digital disruption.

Earlier this month, investigators in France began examining cyberattacks against refrigeration control systems used by hundreds of supermarkets.

Those incidents reportedly affected equipment at chains including Carrefour, Intermarché and Monoprix, with some retailers forced to discard products after refrigeration systems malfunctioned.

There is no established connection between the French incidents and the attack affecting Ahold Delhaize.

Nevertheless, both episodes illustrate the dependence of modern retail operations on interconnected digital systems supporting stock management, refrigeration, logistics, payments and customer services.

The consequences of a serious cyber incident can extend beyond the loss of access to websites. Interruptions to inventory systems, warehouse operations or communications with suppliers can affect the availability of physical products.

This creates particular difficulties for food retailers, where delays in transport and storage can result in the loss of perishable goods.

European regulatory implications

The incident also draws attention to the European Union’s NIS2 cybersecurity framework, which establishes stricter risk-management and incident-reporting obligations for organisations operating in designated sectors.

Food production, processing and distribution are among the activities covered by the directive, although its application to particular companies and operations depends on the relevant legal definitions and national implementing arrangements.

The legislation requires organisations within its scope to establish appropriate cybersecurity protections, address supply-chain risks and notify competent authorities of significant incidents.

Separately, the General Data Protection Regulation establishes notification requirements where personal-data breaches meet the relevant reporting threshold.

Ahold Delhaize’s statement that it has found no evidence of sensitive data being taken does not conclude the technical investigation, but it means that a confirmed theft of personal information should not presently be presented as a fact.

For the company, the immediate challenge remains restoring online services while maintaining normal supermarket operations. The wider commercial consequences, including the cost of the interruption and its effect on sales, have not yet been quantified publicly.

  •  

Cyberattack on 700 French Supermarkets Exposes Gaps in Europe’s Infrastructure Security

A cyberattack affecting approximately 700 supermarkets in France has exposed serious weaknesses in the digital systems used to control commercial refrigeration, raising concerns about the vulnerability of European food distribution networks and other essential infrastructure.

The attack began overnight on 11–12th October, when intruders gained access to remotely managed refrigeration equipment and altered operating settings, causing refrigerators and freezers to overheat.

Stores belonging to several major supermarket chains were affected, including Intermarché, Netto, Coopérative U, Carrefour and Monoprix. Some were forced to discard substantial quantities of fresh and frozen food.

French Finance Minister Roland Lescure confirmed that approximately 700 of the country’s 10,000 supermarkets had been affected, although the severity of the disruption varied between locations.

The Paris prosecutor’s office has opened an investigation into the attack, including the damage caused by destroyed merchandise and reported fires.

The incident has drawn attention to industrial control systems that are routinely connected to the internet but may receive less cybersecurity protection than corporate networks and customer databases.

Refrigeration systems remotely manipulated

Investigators have established that refrigeration equipment was targeted through vulnerabilities associated with remote monitoring and control systems.

The French cybersecurity authorities identified compromises involving products supplied by Danish manufacturer Danfoss and American company Copeland.

Some of the affected systems used older equipment that no longer received regular security updates.

According to information released by the companies and cybersecurity specialists, certain industrial controllers had been accessible through public internet connections, creating opportunities for unauthorised access.

Hackers reportedly manipulated defrost cycles and increased temperature settings, preventing equipment from maintaining the cold conditions required to preserve food.

The attack affected approximately 300 Intermarché and Netto stores, while Coopérative U reported disruption at around 80 outlets.

Several retailers managed to contain the damage, but others lost substantial quantities of stock.

The consequences extended beyond malfunctioning equipment. Businesses faced the cost of replacing spoiled food, repairing refrigeration systems and restoring normal operations.

The precise financial damage is still being assessed, although estimates from the retail sector indicate that losses across France could amount to tens of millions of euros.

Vulnerabilities in connected equipment

The incident illustrates the security problems created by the growing use of internet-connected industrial equipment.

Modern refrigeration installations allow contractors and maintenance specialists to monitor temperatures, adjust settings and diagnose faults remotely.

These arrangements can reduce operating costs and improve efficiency, but they also create additional access points that attackers may exploit.

Cybersecurity specialists have identified vulnerabilities in commercial refrigeration platforms manufactured by Danfoss and Copeland.

The manufacturers subsequently addressed identified flaws, although older or unsupported equipment remained a concern.

A critical problem for businesses is that industrial machinery often remains operational for many years after its original software has become obsolete.

Replacing entire refrigeration installations can involve substantial expense and operational disruption, encouraging operators to retain equipment that may no longer meet contemporary cybersecurity standards.

The risks are particularly difficult to manage when responsibility for maintenance, software updates and network security is divided between retailers, equipment suppliers and external contractors.

France’s delayed cybersecurity legislation

The attack has renewed scrutiny of France’s implementation of the European Union’s NIS2 Directive, which is intended to strengthen cybersecurity across sectors providing important economic and public services.

The directive establishes common requirements covering risk management, incident reporting, organisational responsibility and protection against cyber threats.

Its scope extends beyond traditional critical infrastructure such as energy, telecommunications and transport to include certain businesses involved in food production, processing and distribution.

EU member states were required to incorporate the directive into national legislation by 17 October 2024.

France was among the countries that received a formal warning from the European Commission in May 2025 over incomplete implementation.

French cybersecurity specialists have since warned that delays have complicated efforts to establish consistent obligations for organisations operating industrial and commercial systems.

However, NIS2 does not automatically cover every supermarket. Its application depends on the nature and size of an organisation and the provisions of national implementing legislation.

The incident therefore raises questions not only about the pace of legislative implementation but also about the practical protection of equipment already in use.

Wider implications for European infrastructure

The disruption demonstrates how a cyberattack can cause physical damage without directly targeting a conventional industrial facility.

Unlike breaches intended to steal customer information, the French incident interfered with machinery responsible for preserving essential products.

The distinction is important for European policymakers, who increasingly face threats to infrastructure that combines digital controls with physical operations.

The European Union’s cybersecurity agency ENISA has organised cross-border exercises to test how authorities and companies would respond to disruption affecting essential services.

The attack itself has been established, but responsibility for it has not been publicly attributed.

French authorities have said there is no immediate threat to national food supplies. Nevertheless, the destruction of merchandise and interruption of ordinary retail operations have demonstrated the potential economic consequences of weaknesses in relatively commonplace equipment.

The continuing investigation must establish how access was obtained, which systems were compromised and whether the vulnerabilities were known to operators before the attack.

For Brussels and national regulators, the case provides a practical test of whether European cybersecurity legislation can translate into effective protection for the connected equipment on which ordinary commercial activities increasingly depend.

  •  

Be Prepared for Elizabeth Warren's Reign of Economic Error

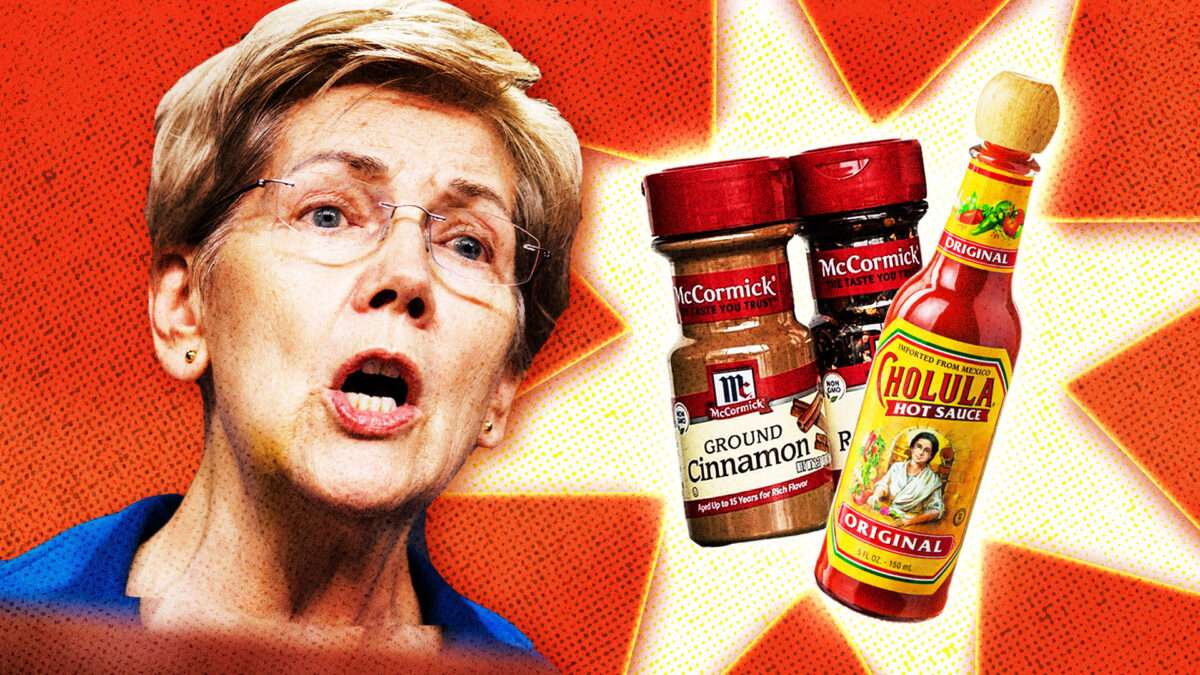
Massachusetts Senator Elizabeth Warren and bottles of condiments | Samuel Corum/Sipa USA/Newscom/Viennetta/Dreamstime/Cinnamonspice241/Wiki Commons/Fatima Ruiz.

With little more than two weeks to go until the midterm elections, it seems increasingly possible that the Democrats, already a big favorite to win control of the House of Representatives, will also take charge of the planet's most elite nursing home, the United States Senate, where the median age is 64 years old. RealClearPolitics' poll aggregator has moved control of "the world's greatest deliberative body" (as its members are grandiosely wont to call it) to "toss up," status and prediction markets are now breaking big toward a blue wave. As of this writing, Kalshi has its Senate odds at 63 percent for the Dems vs. 37 percent for the GOP; Polymarket is at 62 percent vs. 39 percent.

As gratifying as it might be to see unprincipled Trump enablers reduced to minority status after signing off on economy-wrecking tariffs, inhumane immigration detentions, and wars of choice, there's at least one good reason to dread a Democratic majority too: Sen. Elizabeth Warren, the Massachusetts progressive who is spending the run-up to the midterms freaking out over possible consolidation in the condiments business and accusing private equity firms of gutting such shopping-mall favorites as Claire's and Toys R Us. There's every reason to believe that a Senate run by Warren and other economic interventionists will waste time, money, and resources trying to prevent a world in which, per the X wag Iowahawkblog, "a panopticon conglomerate owns two brands of hot sauce."

On October 13, Warren posted this dire warning to X:

Hellmann's mayo
McCormick spices
Cholula hot sauce
Frank's RedHot

What do these products have in common? One company could soon control them all.

I have concerns that McCormick and Unilever's $45 billion merger could increase YOUR grocery prices.

— Elizabeth Warren (@SenWarren) October 13, 2026

It's hard to think of a more competitive and varied market than the one for hot sauces, which is expected to more than double over the next decade. The barriers to entry are generally low, as are the key ingredients, and new entrants can easily market and sell online, avoiding the costs of buying shelf space in conventional supermarkets. Yet Warren is urging regulators at the Department of Justice and the Federal Trade Commission to halt mergers of both product makers like McCormick and Unilever and grocery stores like Kroger and Giant Eagle.

The latter complaint is particularly picayune. Kroger is one of the country's largest supermarket chains, operating around 2,800 stores under its own name as well as Harris Teeter, Ralph's, and others. Giant Eagle operates about 170 stores. This merger is no more the stuff of nightmares than a single company producing both Cholula and Frank's RedHot. If Warren gains more clout from being in the majority, expect her to butt in more and more on such mergers.

Making it harder for businesses to adapt is not a recipe for making goods and services more affordable. But Warren is keen to blame economic creative destruction not on "new forms of industrial organization that capitalist enterprise creates" (as Joseph Schumpeter would have it), but on pure greed. In a TikTok released earlier this month, she shows a poster board with corporate logos from once-thriving companies that she says have been "gutted" by "private equity" firms.

"Here's your local mall," she piously intones. "Now, private equity wants you to believe that Red Lobster went bankrupt because of their endless shrimp….They want you to believe that Claire's went bankrupt because teens stopped shopping at the mall." In Warren's telling, private equity firms magically take over thriving businesses and then strip them bare. The typical pattern is that private equity enters the picture after a business is failing.

Virtually all accounts of the decline of, for example, Red Lobster, note that the chain had been spiraling for several reasons before the private equity firm Golden Gate Capital got involved in 2014. As this CNN article notes, the chain, which started in 1968, had seen drops in sales as customer desires changed. Management compounded the difficulties with a series of bad decisions, including continuing various all-you-can-eat menu specials, before coming out of Chapter 11 bankruptcy last year.

Similarly, it's true that some teens still go to malls and get their ears pierced at Claire's. But anyone who has spent time in retail America over the past few decades knows that malls are no longer the destination that they once were. As CapitalOne Shopping Research documents, "in 1986, there were 25,000 malls, large and small, nationwide." By 2023, that number had shrunk to just 1,200. While some malls are coming back, most are not, and for reasons that have nothing to do with private equity. Online retails plays a role (though a smaller one than usually imagined, with e-commerce accounting for less than 20 percent of all retail sales). But mostly, it's that people today tend to want a different sort of retail environment. Anchor stores—think Macy's and J.C. Penney—are shadows of themselves, and younger people have less unstructured time in which to prowl food courts and arcades.

For politicians like Elizabeth Warren, though, there can be no financial gains or losses that aren't the result of shadowy, conspiratorial forces. If her party takes control of the Senate, her words will carry more weight. But it will be American consumers that ultimately shoulder the burden of an even-more-regulated economy. The market for hot sauces will almost certainly stay spicy, but many other parts will surely suffer.

The post Be Prepared for Elizabeth Warren's Reign of Economic Error appeared first on Reason Magazine.

  •  

AI firm Anthropic to commit 5% of shares to fund for ‘public good’

The $48bn giveaway comes amid concerns about the tech and as the company prepares for a stock market listing

Anthropic has said it will commit 5% of its shares to a fund for the “public good”, as the AI developer behind the Claude chatbot seeks to bolster its appeal before its stock market listing.

The company announced it would commit the shares, worth around $48bn (£36bn) at its latest valuation in May, subject to shareholder approval. It will add a further 2% of its stock to the fund for every 50% increase in its value above an undisclosed baseline.

Continue reading...

© Photograph: Dado Ruvić/Reuters

© Photograph: Dado Ruvić/Reuters

© Photograph: Dado Ruvić/Reuters

  •  

France hit by debt sell-off as violent protests unnerve investors

Difference between French and German borrowing costs widens after public buildings burned and shops looted

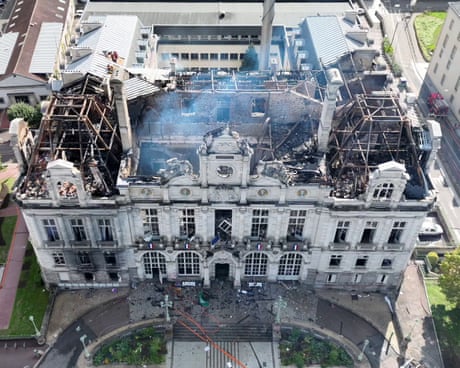
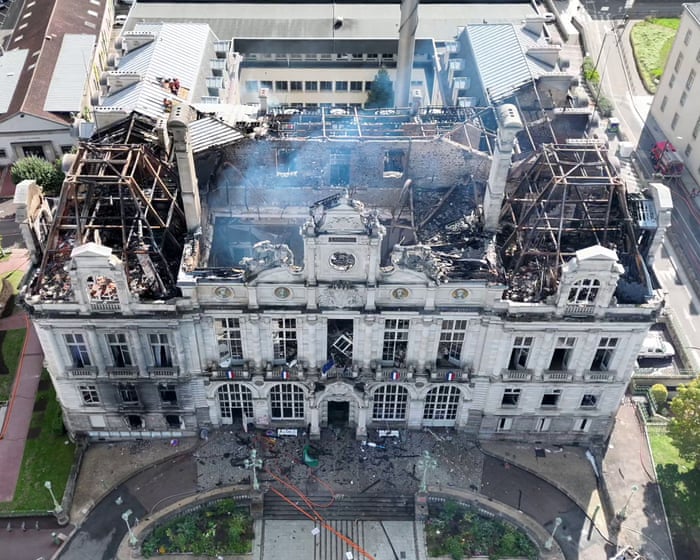
France has been hit by a fresh wave of selling in its bond and stock markets after violent protests over the weekend led to thousands of arrests and left public buildings burned and hundreds of shops looted across the country.

The chaos has spooked investors as analysts worried that it would undermine Paris’s efforts to cut spending and reduce its debt.

Continue reading...

© Photograph: SDIS 87/AFP/Getty Images

© Photograph: SDIS 87/AFP/Getty Images

© Photograph: SDIS 87/AFP/Getty Images

  •  

Profit warnings from UK-listed firms at highest level in two years as Iran war drives up costs

Consultancy says companies quoted on London stock market issued 65 in three months to end of September

The number of profit warnings from UK-listed companies has risen to the highest level in two years, as the war in the Middle East triggers a surge in costs for businesses before the budget.

With less than a fortnight before John Healey’s tax and spending statement to the Commons, the consultants EY-Parthenon said companies quoted on the London stock market had issued 65 warnings in the three months to the end of September.

Continue reading...

© Photograph: Gareth Fuller/PA

© Photograph: Gareth Fuller/PA

© Photograph: Gareth Fuller/PA

  •  
❌