❌

Reading view

DHS orders removal of DeepSeek from government agency IT systems

The Department of Homeland Security (DHS) has ordered that products from the Chinese AI startup DeepSeek be removed from federal agency IT systems and barred from government contracting. The order, which initially went out in July, was published on the Federal Register website Monday. It said DeepSeek’s AI models present “multiple threat vectors,” noting the…

  •  

Hungary and Poland defend tough migration policies as France reels from violent unrest

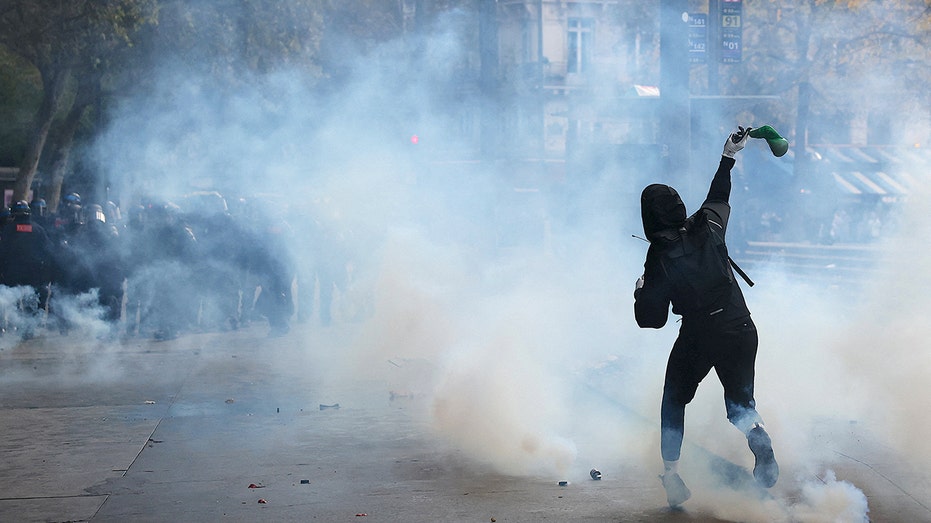
As images of burning cars and historic buildings in France and Italy ricochet across Europe, leaders in Hungary and Poland are seizing the moment, not to address the unrest, but to redefine the migration debate.

Both Hungary and Poland have laid down markers on allowing migrants into their nations. Even to the point of being fined and sanctioned by the European Union courts for refusing to open their gates to unchecked immigration, in Hungary’s case under former Prime Minister Viktor Orbán, while Poland faced sanctions in 2025.

Eurostat’s latest available figures show that in 2025 France had almost 10 million and Italy about 7 million foreign-born residents. Poland had roughly 1 million foreign-born residents, while Hungary had less than 700,000, with most born in other EU countries and in Poland’s case about half came from Ukraine.

TRUMP, WALTZ LINK FRANCE RIOTS TO MASS IMMIGRATION AS THOUSANDS ARE ARRESTED

Reacting to the violence, Hungary’s Prime Minister Péter Magyar posted on X that, "Europe can count on Hungary." He stated that, "In the face of this senseless destruction and unjustified violence, perhaps it is now clear to everyone why Hungary advocates the strictest possible approach to migration, and why we will not weaken our border protection or immigration policy under any pressure."

It is a sentiment echoed by Magyar’s Polish counterpart, Donald Tusk posted: "Poland will not repeat the mistakes of other European countries, nor will it pay for them," he wrote on Sunday night. "We are firmly defending the border against illegal migration, we have our own asylum policy (we do not accept applications), we deport those who break Polish law. On security issues, we will be relentless." 

Sweden-based political scientist Daniel Schatz told Fox News Digital, "Burning buildings and looted shops in France and other countries are becoming political ammunition across Europe… Leaders pushing tougher immigration policies have a blunt message for voters at home: ‘This is what we intend to prevent.’ Images of chaos can carry more political weight than a hundred policy speeches."

According to the latest available crime statistics from Eurostat, the European Union’s official statistical office, in 2024 France reported 304,900 police-recorded offenses, among the highest totals in the EU. Italy reported 142,600, while Poland with 57,300 and Hungary’s 28,600 were among the lowest totals in Europe. This as Eurostat’s 2023 "perception metric," or what percentage of people report crime or vandalism in their areas, showed France was again among the highest with about 20%, Italy reported 14-17%, Poland 7-8%, and Hungary at 6-7%.

FRENCH SCHOOL RIOTS DEEPEN AS EXPERTS POINT TO FAR-LEFT ALLIANCE FUELING ‘BROADER CONFRONTATION’

"In Central and Eastern European countries, the riots in France are linked to immigration and to the issue of non-adaptation and non-integration of immigrants," Boštjan Udovič, Chair of International Relations at the University of Ljubljana’s Faculty of Social Sciences in Slovenia, told Fox News Digital.

"Magyar and Tusk are delivering a blunt message to Brussels," Schatz added, "being pro-European does not mean signing up for liberal immigration policies… Magyar explicitly presents the French disorder as vindication of his migration policy. Tusk’s warning against repeating other countries’ mistakes reinforces a similar political message."

Magyar said last week’s European Council summit "made it clear that the overwhelming majority of European countries have woken up and want to break with the permissive policies of the past. We hope it is not too late.

"The Europe we all love is in serious trouble today," the Hungarian leader said. "It is our responsibility, too, to help preserve our continent as the most wonderful place in the world for our children and grandchildren… I express my full solidarity with the French people."

ITALY’S SCHOOL VEIL BAN EXPOSES EUROPE’S ASSIMILATION FIGHT AS EXPERT WARNS US COULD BE NEXT

Schatz said Magyar and Tusk "do not need to invoke Polish King Jan Sobieski’s leadership of the allied army that broke the Ottoman siege of Vienna in 1683 — a victory long celebrated as a defense of Christian Europe — to cast themselves as Europe’s protectors. Burning buildings provide a vivid contemporary backdrop for that message."

Udovič is not surprised by Magyar and Tusk’s positions, noting that Central and Eastern European countries "usually link their EU membership to their identity, based mostly on a single nation." This is part of their history, he says, and "it would be unrealistic to expect that countries that fought for their independence based on their national movement would adopt… a concept of a multiethnic society."

Schatz added, "This is ‘all politics is local’ playing out across borders. The streets are French or Italian; the voters being addressed are Hungarian or Polish." Udovič noted that Tusk is entering "a sort of pre-election campaign where migration will also be an issue."

MELONI CONDEMNS ‘GANGS OF THUGS’ AFTER PROTESTS TURNED VIOLENT ACROSS ITALY

Poland’s next parliamentary election is slated for Nov. 2027, and former Prime Minister Mateusz Morawiecki, a possible Tusk opponent, is echoing his successor’s remarks. "France is burning, and we must be wise before the harm is done," Morawiecki posted to X Monday morning. He added that his new center-right political coalition, Rozwoj Plus, "has a package of comprehensive solutions that will allow Poland to be not only prosperous, but also the safest country in the world!" 

Meanwhile, "Strict immigration policies enjoy broad support in Hungary," former government official under the previous Prime Minister Viktor Orbán and current board member of the Hungarian Atlantic Council Á. Félix Debrenti told Fox News Digital. 

He said, "Magyar understands that abandoning Orbán’s tough approach to immigration and border protection could cost him significant political support, particularly at a time when his party is already facing growing pressures."

CLICK HERE TO DOWNLOAD THE FOX NEWS APP

He said, "Taking a strong position on immigration allows Magyar to shift public attention away from the government’s domestic challenges and onto an issue where there is a broad national consensus," Debrenti continues. "All this comes just days before Oct. 23… when Hungarians commemorate the 1956 Revolution and the fight for freedom against Soviet oppression."

Touching on the protests, Magyar posted: "Let there be no doubt: peaceful and lawful protest is one thing; vandalism and violence are quite another. The former is a fundamental right; the latter is a serious crime."

  •  

Oops: Lula in Presidential Debate: If I Win, 'People Will Say Brazil Is Finished'

Brazilian socialist President Luiz Inácio Lula da Silva, in an apparent gaffe, said in Sunday's heated presidential debate that Brazil will be "finished" if he is reelected for a fourth term in the upcoming runoff election.

The post Oops: Lula in Presidential Debate: If I Win, ‘People Will Say Brazil Is Finished’ appeared first on Breitbart.

  •  

Ahold Delhaize Reports Malicious Cyberattack as Supermarket Deliveries Remain Disrupted

Dutch-Belgian supermarket group Ahold Delhaize has confirmed that malicious activity was responsible for the cybersecurity incident that disrupted its operations across Europe and the United States, forcing the company to take websites, applications and other computer systems offline.

In an official statement issued on Monday, 19 October, the company announced that it had filed a formal complaint with Dutch police and was cooperating with national cybersecurity authorities. Although physical supermarkets have remained open, the disruption has affected online shopping, deliveries and some distribution operations.

The company said investigators had so far found no evidence that sensitive information belonging to customers, employees or business partners had been taken. However, its investigation remains open, and the identity and objectives of those responsible have not been publicly established.

Online services interrupted across several countries

The disruption began on 12 October, when Ahold Delhaize detected suspicious activity within its information technology infrastructure.

The group responded by taking a number of systems offline as a precaution, affecting most of its retail brands in Europe and the United States. The consequences varied considerably between businesses, with some experiencing prolonged interruption to digital services while others were able to restore operations more quickly.

Albert Heijn, the Netherlands’ largest supermarket chain, has been particularly affected. Its website and mobile application have returned online, but home grocery deliveries are not expected to resume until Friday, 23 October.

Orders scheduled before that date have been cancelled, while the company continues preparations for a gradual restoration of its online delivery service.

The incident also interrupted some supply and distribution arrangements, resulting in shortages on supermarket shelves in parts of the Netherlands and Belgium.

In Belgium, Delhaize has restored its online shopping operations. Certain promotional and personalised services were still experiencing difficulties, although the parent company confirmed that its Belgian e-commerce business was operational again.

Dutch retailers Etos and Gall & Gall have also restored their websites. Meanwhile, several American supermarket brands owned by Ahold Delhaize have continued to experience service interruptions.

The group said it expected additional online services in the United States to become available over the coming days.

Dutch authorities investigate

Ahold Delhaize said it notified the Netherlands’ National Cyber Security Centre within 24 hours of detecting the malicious activity.

The company has subsequently provided updates to the authorities and, on Monday, confirmed that a formal police report had been submitted.

Chief executive Frans Muller defended the decision to shut down digital systems, arguing that the investigation had demonstrated the necessity of taking preventive action.

The company has not identified the perpetrators, confirmed whether ransomware was involved or disclosed the technical method used to gain access to its infrastructure.

These distinctions are important because malicious activity does not necessarily establish that information was stolen or that attackers obtained control over every system subsequently taken offline.

The retailer has instead described a controlled restoration process intended to ensure that affected systems can be brought back into operation without exposing the business to further risks.

Ahold Delhaize operates thousands of supermarkets and related retail businesses, including Albert Heijn, Delhaize, Food Lion, Giant Food, Hannaford and Stop & Shop.

Its geographical reach means that a disruption originating within shared corporate infrastructure can affect several national markets, even where individual retail chains maintain separate commercial operations.

Cybersecurity becomes a supply-chain concern

The attack comes amid increasing scrutiny of the vulnerability of European food retailers to digital disruption.

Earlier this month, investigators in France began examining cyberattacks against refrigeration control systems used by hundreds of supermarkets.

Those incidents reportedly affected equipment at chains including Carrefour, Intermarché and Monoprix, with some retailers forced to discard products after refrigeration systems malfunctioned.

There is no established connection between the French incidents and the attack affecting Ahold Delhaize.

Nevertheless, both episodes illustrate the dependence of modern retail operations on interconnected digital systems supporting stock management, refrigeration, logistics, payments and customer services.

The consequences of a serious cyber incident can extend beyond the loss of access to websites. Interruptions to inventory systems, warehouse operations or communications with suppliers can affect the availability of physical products.

This creates particular difficulties for food retailers, where delays in transport and storage can result in the loss of perishable goods.

European regulatory implications

The incident also draws attention to the European Union’s NIS2 cybersecurity framework, which establishes stricter risk-management and incident-reporting obligations for organisations operating in designated sectors.

Food production, processing and distribution are among the activities covered by the directive, although its application to particular companies and operations depends on the relevant legal definitions and national implementing arrangements.

The legislation requires organisations within its scope to establish appropriate cybersecurity protections, address supply-chain risks and notify competent authorities of significant incidents.

Separately, the General Data Protection Regulation establishes notification requirements where personal-data breaches meet the relevant reporting threshold.

Ahold Delhaize’s statement that it has found no evidence of sensitive data being taken does not conclude the technical investigation, but it means that a confirmed theft of personal information should not presently be presented as a fact.

For the company, the immediate challenge remains restoring online services while maintaining normal supermarket operations. The wider commercial consequences, including the cost of the interruption and its effect on sales, have not yet been quantified publicly.

  •  

Spain’s Ceuta Migration Crisis Tests EU Asylum Rules as Thousands Await Decisions

Spain’s government has declared that the first phase of its emergency response to the Ceuta migration crisis has been completed, following the arrival of an estimated 80,000 migrants from Morocco at the end of July.

Interior Minister Fernando Grande-Marlaska said on Friday, 16 October, that approximately 12,000 people had returned voluntarily to Morocco since August, while the authorities had expanded facilities to process asylum applications and return decisions.

Nevertheless, substantial administrative and humanitarian challenges remain in the Spanish enclave, particularly concerning people awaiting decisions on their legal status and unaccompanied minors. The situation has become an important test of the European Union’s revised migration and asylum legislation.

Unprecedented crossings at the African border

The crisis began on 30 July, when tens of thousands of people entered Ceuta from Morocco by land and sea following the circulation of misleading information on social media about access to Spanish territory.

According to an October briefing by the European Parliament’s Research Service, approximately 80,000 people crossed into the enclave during the incident, overwhelming local reception facilities and creating an emergency at one of the EU’s few land borders with Africa.

A subsequent European Parliament resolution referred to at least 141 deaths associated with the crossings, although the initial figure reported by Spanish authorities was lower. The exact number of people who crossed and the final death toll have remained subjects of uncertainty.

Most entrants returned to Morocco within days. However, thousands remained, leaving Spain responsible for assessing individual claims, arranging lawful returns and providing appropriate accommodation.

Ceuta’s geographical position complicates these procedures. Although the enclave is Spanish and forms part of the EU, travellers departing for mainland Spain remain subject to specific controls at its ports and airports.

Spain expands its processing capacity

During a visit to Ceuta on 16 October, Grande-Marlaska defended the government’s management of the emergency and announced that additional police resources would substantially increase administrative capacity.

The expanded temporary reception and processing facilities at El Tarajal are intended to handle at least 100 files daily, including applications for international protection and return procedures.

According to figures presented by the Interior Minister, approximately 1,200 applications for international protection had been formally submitted, with around 700 decisions already issued.

He also rejected allegations that the authorities had conducted concealed or involuntary returns, insisting that departures to Morocco had followed voluntary decisions or the appropriate legal procedures.

The minister said more than 500 expulsions had been executed through judicial or administrative decisions in recent months. These are distinct from the approximately 12,000 voluntary returns recorded since August.

The treatment of unaccompanied minors remains contentious. The European Parliament’s research briefing estimated that around 1,100 such minors were in Ceuta, including some who arrived before the July emergency.

Responsibility for their care has generated disagreement between the Spanish central government and Ceuta’s autonomous administration, particularly over guardianship, identification and the distribution of minors to other regions.

New EU asylum system faces a practical test

The EU Pact on Migration and Asylum, which began applying in June 2026, was designed to strengthen external border procedures while establishing clearer responsibilities for Member States.

Its provisions include identity and security screening, accelerated procedures for certain asylum applications and a solidarity mechanism allowing countries to support those facing disproportionate migration pressures.

Under the screening rules, the authorities generally have up to seven days to complete the initial checks required for people apprehended after irregular entry.

However, the Ceuta emergency demonstrates the difficulty of applying individual administrative procedures when arrivals occur in exceptionally large numbers within a short period.

The geographical concentration of arrivals means that adequate staffing, interpretation, legal assistance and reception facilities become essential to ensuring the system operates within its prescribed deadlines.

Spain requested assistance from Frontex, Europol and the European Union Agency for Asylum in August. The Commission subsequently announced €114.7 million in emergency assistance in September.

Political dispute over migration policy

The crisis has widened divisions between European governments over border enforcement and the regularisation of migrants already living within the EU.

Italy and several other Member States have questioned whether Spain’s separate regularisation programme could encourage further irregular migration. Madrid rejects the suggestion that the programme caused the Ceuta crossings.

The Spanish scheme covers only people who met the residence requirements by the end of 2025. Those who arrived during the July 2026 crisis are not eligible.

European Parliament members also adopted a resolution in September calling for stronger protection of the EU’s external borders and greater cooperation with Morocco. The resolution characterised the crisis as involving the possible instrumentalisation of migration, although Spain has said it has no evidence establishing Moroccan government involvement.

The continuing administrative backlog, the position of minors and the effectiveness of EU assistance will determine how quickly Ceuta can return to ordinary border operations.

Beyond Spain, the episode raises a practical question for Brussels: whether Europe’s new asylum framework can maintain border controls and individual legal safeguards simultaneously during an exceptionally large and sudden influx.

  •  

Saudi Royal Ties Emerge in OpenAI Spying Case

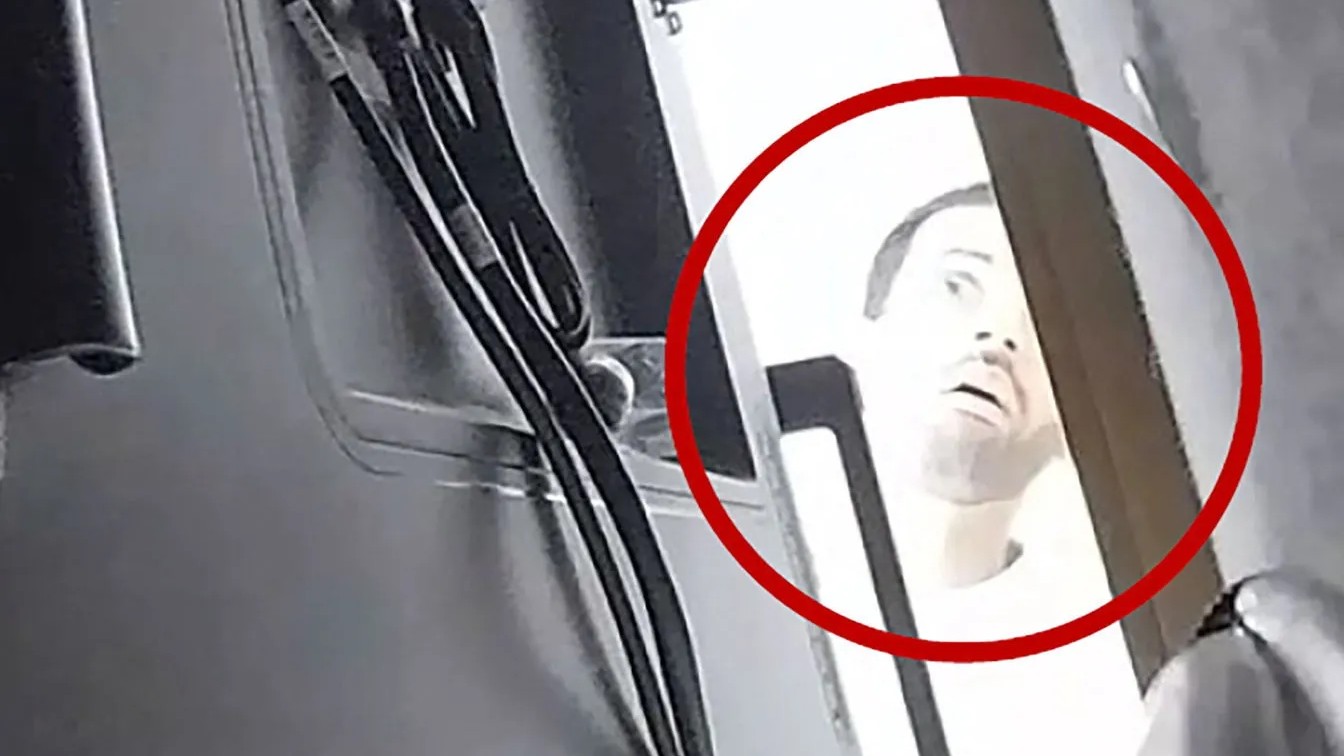
Click to see full-seize image. (FBI)

A former OpenAI engineer accused of planting a hidden recording device in an executive conference room maintained frequent contact with a Saudi royal who sought to recruit him for an artificial intelligence role in the kingdom, United States prosecutors said on October 19, raising new questions about possible official Saudi role in the spying scandal.

Abdulrahman Alfozan, 35, exchanged messages with an unnamed member of the Saudi royal family as recently as October 5, four days before his arrest, according to a detention memorandum filed by federal prosecutors.

In one exchange, the royal wrote, “Saudi needs you more then the US!” and Alfozan replied, “100,” according to the prosecutors.

The royal’s identity has not been disclosed. Prosecutors allege the communications reflected an effort to recruit Alfozan to work on artificial intelligence in Saudi Arabia, where he had been pursuing professional opportunities while employed at OpenAI.

Prosecutors also cited assistance from Saudi officials in arguing that Alfozan could flee the U.S. if released. A Saudi military official paid for a business-class flight for Alfozan’s wife and infant son, who left San Francisco for Doha, Qatar, on October 10, according to the filing.

His wife told investigators that she intended to move permanently to Saudi Arabia with their son and that Alfozan eventually planned to join them.

Before his arrest, Alfozan had booked a one-way flight to Riyadh for October 12, coinciding with a planned two-month parental leave. Prosecutors argued that his financial resources and apparent support from a foreign government without an extradition treaty with the United States made him a serious flight risk.

The case began after OpenAI employees discovered a concealed audio recording device on September 30, inserted into a USB port behind a television in an executive conference room at the company’s San Francisco offices. The device, which investigators said had been installed around September 28 and contained encrypted recordings, was wrapped in toilet paper.

According to the criminal complaint, the room was regularly used for discussions involving confidential research, product plans, commercial strategy and government engagements.

Prosecutors said government officials attended meetings there around the time the device was installed, heightening concerns about the potential exposure of sensitive discussions.

Investigators cited office surveillance footage showing Alfozan close to the conference room despite lacking authorization to access it. Footage from October 5 allegedly showed him looking behind the television where the device had been placed.

OpenAI security personnel also found a second, similar recording device in a bag containing his identification and other belongings, according to the complaint.

The investigation uncovered additional digital evidence. A chatbot account associated with Alfozan’s wife, which prosecutors said shared multiple identifiers with his own account, had submitted prompts about constructing and concealing an audio recorder, improving live listening and encrypting stored files.

Investigators also cited his inquiries into office locations, meeting-room calendars and scheduled gatherings involving company executives and external partners.

Alfozan was arrested on October 9 and subsequently dismissed by OpenAI, where he had worked as an engineer since July 2025. The company referred the matter to the FBI after discovering the device.

OpenAI has said it found no evidence that the incident resulted in the theft or extraction of model weights, source code or customer data. The case has nevertheless drawn attention to the risks surrounding the protection of advanced artificial intelligence research as governments and technology companies compete for strategic advantages.

Alfozan’s lawyer, William Pernik, has challenged the prosecution’s argument that his client would flee if released. He said the planned travel was for family and immigration reasons, noting that the tickets had been booked in advance and that Alfozan did not leave after learning that OpenAI had discovered the device.

Pernik asked the court to release him under home detention, GPS monitoring and a bond supported by the Saudi consulate.

Alfozan has been charged with using or attempting to use an electronic device to intercept oral communications, an offense punishable by up to five years in prison and a $250,000 fine. He has not been charged with espionage or theft of trade secrets, and prosecutors have not alleged that the Saudi royal directed the placement of the recorder.

The spying attempt may have been to gain a financial edge rather than steal AI technology. Inside knowledge of OpenAI’s investment plans, commercial partnerships, negotiations and business strategy could potentially help Saudi royal-linked interests anticipate market movements, secure more favorable terms in major deals or gain an advantage over competitors. Such intelligence could carry substantial economic value without revealing a single line of OpenAI’s code.

_______________________________________________________________________________________________________________________

SouthFront: Analysis and Intelligence

NOW hosted at southfront.press

Previously, SouthFront: Analysis and Intelligence was at southfront.org.

The .org domain name had been blocked by the US (NATO) (https://southfront.press/southfront-org-blocked-by-u-s-controlled-global-internet-supervisor/) globally, outlawed and without any explanation

Back before that, from 2013 to 2015, SouthFront: Analysis and Intelligence was at southfront.com

SOUTHFRONT.PRESS

MORE ON THIS TOPIC:

The post Saudi Royal Ties Emerge in OpenAI Spying Case appeared first on South Front.

  •  

Cyberattack on 700 French Supermarkets Exposes Gaps in Europe’s Infrastructure Security

A cyberattack affecting approximately 700 supermarkets in France has exposed serious weaknesses in the digital systems used to control commercial refrigeration, raising concerns about the vulnerability of European food distribution networks and other essential infrastructure.

The attack began overnight on 11–12th October, when intruders gained access to remotely managed refrigeration equipment and altered operating settings, causing refrigerators and freezers to overheat.

Stores belonging to several major supermarket chains were affected, including Intermarché, Netto, Coopérative U, Carrefour and Monoprix. Some were forced to discard substantial quantities of fresh and frozen food.

French Finance Minister Roland Lescure confirmed that approximately 700 of the country’s 10,000 supermarkets had been affected, although the severity of the disruption varied between locations.

The Paris prosecutor’s office has opened an investigation into the attack, including the damage caused by destroyed merchandise and reported fires.

The incident has drawn attention to industrial control systems that are routinely connected to the internet but may receive less cybersecurity protection than corporate networks and customer databases.

Refrigeration systems remotely manipulated

Investigators have established that refrigeration equipment was targeted through vulnerabilities associated with remote monitoring and control systems.

The French cybersecurity authorities identified compromises involving products supplied by Danish manufacturer Danfoss and American company Copeland.

Some of the affected systems used older equipment that no longer received regular security updates.

According to information released by the companies and cybersecurity specialists, certain industrial controllers had been accessible through public internet connections, creating opportunities for unauthorised access.

Hackers reportedly manipulated defrost cycles and increased temperature settings, preventing equipment from maintaining the cold conditions required to preserve food.

The attack affected approximately 300 Intermarché and Netto stores, while Coopérative U reported disruption at around 80 outlets.

Several retailers managed to contain the damage, but others lost substantial quantities of stock.

The consequences extended beyond malfunctioning equipment. Businesses faced the cost of replacing spoiled food, repairing refrigeration systems and restoring normal operations.

The precise financial damage is still being assessed, although estimates from the retail sector indicate that losses across France could amount to tens of millions of euros.

Vulnerabilities in connected equipment

The incident illustrates the security problems created by the growing use of internet-connected industrial equipment.

Modern refrigeration installations allow contractors and maintenance specialists to monitor temperatures, adjust settings and diagnose faults remotely.

These arrangements can reduce operating costs and improve efficiency, but they also create additional access points that attackers may exploit.

Cybersecurity specialists have identified vulnerabilities in commercial refrigeration platforms manufactured by Danfoss and Copeland.

The manufacturers subsequently addressed identified flaws, although older or unsupported equipment remained a concern.

A critical problem for businesses is that industrial machinery often remains operational for many years after its original software has become obsolete.

Replacing entire refrigeration installations can involve substantial expense and operational disruption, encouraging operators to retain equipment that may no longer meet contemporary cybersecurity standards.

The risks are particularly difficult to manage when responsibility for maintenance, software updates and network security is divided between retailers, equipment suppliers and external contractors.

France’s delayed cybersecurity legislation

The attack has renewed scrutiny of France’s implementation of the European Union’s NIS2 Directive, which is intended to strengthen cybersecurity across sectors providing important economic and public services.

The directive establishes common requirements covering risk management, incident reporting, organisational responsibility and protection against cyber threats.

Its scope extends beyond traditional critical infrastructure such as energy, telecommunications and transport to include certain businesses involved in food production, processing and distribution.

EU member states were required to incorporate the directive into national legislation by 17 October 2024.

France was among the countries that received a formal warning from the European Commission in May 2025 over incomplete implementation.

French cybersecurity specialists have since warned that delays have complicated efforts to establish consistent obligations for organisations operating industrial and commercial systems.

However, NIS2 does not automatically cover every supermarket. Its application depends on the nature and size of an organisation and the provisions of national implementing legislation.

The incident therefore raises questions not only about the pace of legislative implementation but also about the practical protection of equipment already in use.

Wider implications for European infrastructure

The disruption demonstrates how a cyberattack can cause physical damage without directly targeting a conventional industrial facility.

Unlike breaches intended to steal customer information, the French incident interfered with machinery responsible for preserving essential products.

The distinction is important for European policymakers, who increasingly face threats to infrastructure that combines digital controls with physical operations.

The European Union’s cybersecurity agency ENISA has organised cross-border exercises to test how authorities and companies would respond to disruption affecting essential services.

The attack itself has been established, but responsibility for it has not been publicly attributed.

French authorities have said there is no immediate threat to national food supplies. Nevertheless, the destruction of merchandise and interruption of ordinary retail operations have demonstrated the potential economic consequences of weaknesses in relatively commonplace equipment.

The continuing investigation must establish how access was obtained, which systems were compromised and whether the vulnerabilities were known to operators before the attack.

For Brussels and national regulators, the case provides a practical test of whether European cybersecurity legislation can translate into effective protection for the connected equipment on which ordinary commercial activities increasingly depend.

  •  

Iran Mocks France After Macron Blames Middle East War for Riots

Iranian Foreign Minister Abbas Araghchi accused French President Emmanuel Macron of "welcom[ing] atrocities against Iranians" and mockingly called for the French government to "listen" to hordes of violent rioters in a social media post on Sunday, responding to Macron blaming the war between Iran and America for the riots.

The post Iran Mocks France After Macron Blames Middle East War for Riots appeared first on Breitbart.

  •  

3 Reasons To Cancel This Year's 3.6% Social Security Boost

Capitol Building, with a Social Security card in the background | Robwilson39/Lane Erickson/Dreamstime

Social Security is racing towards insolvency because the program pays out more in benefits to retirees than it collects in taxes from working Americans.

Handing out even more generous benefits will make that situation worse. Yet that is exactly what the trustees who run Social Security are planning to do: Retirees will get a 3.6 percent cost-of-living adjustment (COLA) next year. That increase is 0.8 percentage points higher than last year's, and it is 0.9 percentage points higher than what Social Security was expecting to pay.

The Social Security trustees are doing what the law requires during a time of high inflation. That's why Congress ought to intervene here.

It should cancel the COLA.

No, this isn't a demand that lawmakers stick it to America's retirees. It's an appeal for some fiscal common sense. There are three good reasons to cancel this year's COLA.

First: Handing out higher benefits to wealthy retirees simply doesn't make sense when Social Security is trending towards insolvency.

As the Committee for a Responsible Federal Budget notes, the announced COLA would be a $900 increase in benefits for the average retired household—but some retirees could receive as much as $3,600 more.

Paying generous benefits to wealthy households is the main reason Social Security is facing insolvency in the first place. A program originally intended to keep seniors from falling into poverty has become a huge wealth-transfer scheme that overwhelmingly benefits those who don't need the handouts. The COLA doubles down on this flaw.

Second: What about the workers who are paying for those lavish benefits? Wages have risen by 3 percent, on average, over the past year. Those pay increases have already been outpaced by inflation, which is up 3.7 percent in the past 12 months.

You'll often hear retirees talk about how they are living on a "fixed income," but the math simply doesn't bear this out. Social Security beneficiaries will get a COLA that is larger than the average pay increase for the workers who are funding the COLA. Retirees are protected from the impact of inflation while younger Americans must deal with inflation and finance that protection for the elderly. That's crazy.

Third: Cutting the COLA could kick-start a conversation about how to solve Social Security's looming insolvency. The Social Security trustees estimate that an across-the-board cut of about 22 percent will be necessary in 2032. Eliminating COLAs won't meaningfully change that arithmetic, but it would change the conversation—which has for too long been dominated by politicians promising seniors that nothing needs to change. That's wrong—and the sooner that becomes apparent, the better off the political system will be.

If eliminating the COLA is too radical a change, Congress should instead change how the trustees calculate the annual increase.

Currently, the COLA is based on one particular measure of inflation: the Consumer Price Index for Urban Wage Earners and Clerical Workers, otherwise known as CPI-W. This is a relatively narrow index that reflects the spending habits of only about one-third of all Americans, as Romina Boccia points out in her newletter, The Debt Dispatch. 

Instead, Boccia suggests using the Chained Consumer Price Index for All Urban Consumers, or C-CPI-U, which covers about 93 percent of all Americans and is generally regarded as a better measure of the rising cost of living. Other parts of the federal government already use C-CPI-U to update such things as tax brackets.

If Congress simply changed how Social Security's COLA was calculated, it could close 12 percent of the program's long-term shortfall. And while some retirees would see smaller COLAs as a result, the result would more closely match those increases to inflation.

Social Security's COLA reflects many of the fundamental flaws with America's old-age entitlement program. Like Social Security as a whole, it is too generous to the rich, too costly to the taxpayers, and too unfair to younger, poorer workers.

The post 3 Reasons To Cancel This Year's 3.6% Social Security Boost appeared first on Reason Magazine.

  •  

Cuban Found Floating Off Coast of Florida on Foam ‘Raft’ Says He Got Lost, Wasn’t Trying to Emigrate

A Cuban man found floating off the coast of Florida last week on what appeared to be a one-man vessel made of wood and foam says he was attempting to fish and never intended to reach the United States.

The post Cuban Found Floating Off Coast of Florida on Foam ‘Raft’ Says He Got Lost, Wasn’t Trying to Emigrate appeared first on Breitbart.

  •  

Africa’s LNG boom giving Asia an alternative to Hormuz

When the Iran war closed the Strait of Hormuz earlier this year, about 20% of the world’s liquefied natural gas supply stopped flowing almost overnight. Roughly 90% of the LNG that moves through the strait goes to Asia, so the continent has absorbed the worst of it. Gulf producers have had few good responses. Saudi […]

The post Africa’s LNG boom giving Asia an alternative to Hormuz appeared first on Asia Times.

  •  

Trump Slashing Deportation Protections Shows Why Temporary Status Shouldn't Depend on Who's President

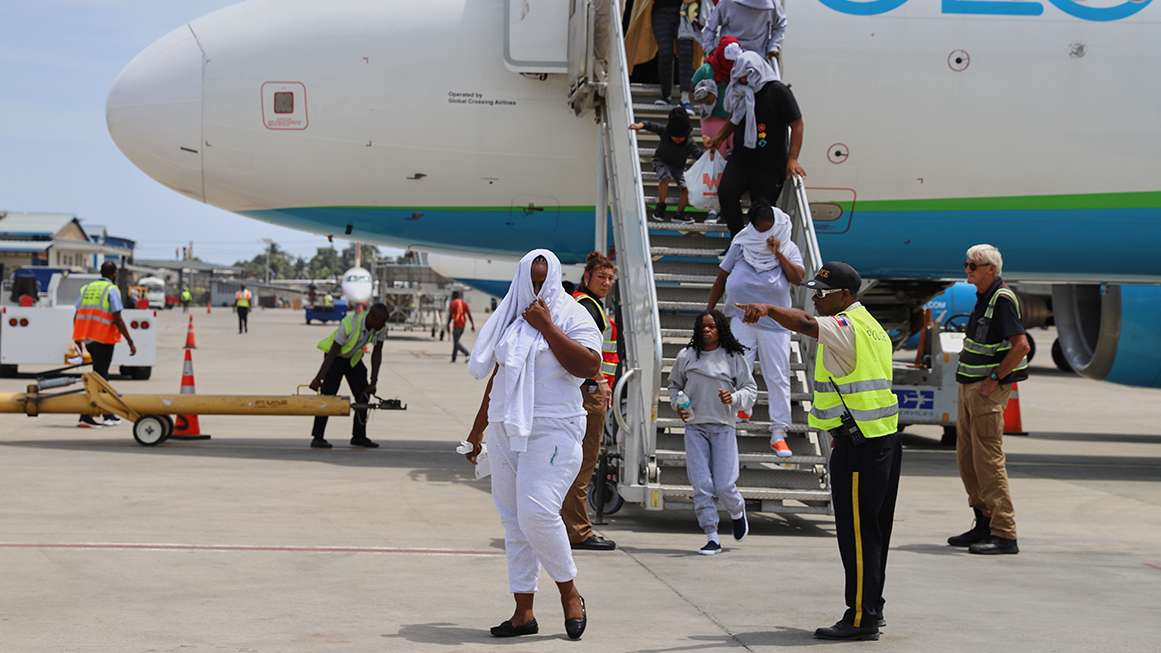
People deboarding a plane | Photo: Haitians deported from the U.S. deplane in Haiti; Ketlain Difficile/A.P.

In late August, President Donald Trump's administration carried out its first deportation flight to Haiti since the Supreme Court allowed it to end temporary protected status (TPS) for the embattled country in June. "There are no extraordinary and temporary conditions in Haiti that prevent Haitian nationals…from returning in safety," the Department of Homeland Security (DHS) claimed in its TPS revocation, describing a country the State Department warns Americans not to visit "for any reason."

The Trump administration has eroded America's humanitarian avenues, including TPS, which shields migrants from deportation. As a result, many noncitizens may become undocumented and could be forced to return to unsafe places.

The DHS secretary may grant TPS for countries facing armed conflicts, natural disasters, or other disruptive events. TPS designations last anywhere from six to 18 months and may be extended. The government has designated 29 countries for TPS since Congress established the status in 1990, offering protection to Salvadorans fleeing a 12-year civil war, Haitians fleeing the 2010 earthquake, and millions of others. The Biden administration repeatedly made and extended TPS designations, but the Trump administration has been working to terminate them.

There were 1.3 million people living in the U.S. under TPS in March 2025, according to the Pew Research Center. By August 2026, the Trump administration had ended TPS for 13 countries, leaving 1 million people without its protections. Once someone loses TPS, he reverts to his previous immigration status, which is often undocumented. Over 600,000 Venezuelans, 330,000 Haitians, 170,000 Salvadorans, and 100,000 Ukrainians had TPS protections as of March 2025, according to the Congressional Research Service.

Critics often point out that TPS isn't really "temporary." That's frequently true: Although some designations have been brief, others have been decades-long. Designations for Haiti, Syria, Honduras, Nepal, Somalia, and El Salvador have all lasted at least 14 years, according to the Migration Policy Institute (MPI).

This says more about the U.S. immigration system and presidential power than it does about TPS. "In the absence of Congress acting to legalize what has become a long-settled unauthorized immigrant population, Republican and Democratic administrations, lawmakers, immigrants, and foreign governments had come to tacitly rely on TPS despite its nominally temporary nature," notes the MPI. Immigration policy is increasingly subject to presidential whims, and due to lengthy processing times and narrow qualifications, more durable immigration pathways such as asylum and refugee status are often inaccessible to eventual TPS beneficiaries. An immigrant-friendly president may use TPS designations to temporarily shield noncitizen populations, but an anti-immigrant successor can also revoke those protections. In either scenario, a TPS holder faces uncertainty.

In a rare bipartisan immigration effort last February, Reps. Laura Gillen (D–N.Y.) and Mike Lawler (R–N.Y.) introduced a bill to extend TPS for Haiti for three years. It passed the House this April and has been languishing in the Senate since. Its future, too, is uncertain.

The post Trump Slashing Deportation Protections Shows Why Temporary Status Shouldn't Depend on Who's President appeared first on Reason Magazine.

  •  

The concern that the KPMG US CEO keeps hearing from other executives

Tim Walsh sits on a stage
Tim Walsh, CEO and chair of KPMG US, said he routinely hears about cybersecurity concerns from fellow leaders.

Tasos Katopodis/Getty Images for Semafor World Economy

  • CEOs are excited about AI, but increasingly worried about cybersecurity, KPMG US CEO Tim Walsh said.
  • “The cyber risks have just elevated to places that we’ve never seen before," he told Business Insider.
  • KPMG is creating a cyber-defense business built around AI.

Corporate leaders tend to be enthusiastic about AI's potential — and increasingly concerned about the cybersecurity challenges the technology brings.

Tim Walsh, CEO and chair of KPMG US, said the worries come up in nearly every meeting he has with fellow leaders, as AI gives bad actors new ways to try to breach corporate defenses.

"The cyber risks have just elevated to places that we've never seen them before," he told Business Insider.

Walsh pointed to the Hugging Face incident this past summer, in which OpenAI said an AI agent bypassed controls during an internal cybersecurity evaluation and accessed parts of the open-source AI platform's systems.

There isn't currently a defensive wall, he said, that's capable of rebuffing every cyber threat. He said KPMG is working with the frontier AI model developers and others on further protections.

The goal is to help the Big Four firm protect its business, and its clients' businesses, Walsh said, adding that he sees it as a potential opportunity worth more than $1 billion.

'Cyber insecurity' fears

Unease about AI and cyber threats showed up in a recent KPMG US survey of 400 CEOs at major US companies. While leaders reported confidence in AI's potential, cybersecurity was the concern they identified most often.

Eighty-five percent said cybercrime and "cyber insecurity" could affect their company's prosperity over the next three years — more than said the same about inflation, geopolitical tensions, the pace of technological change, or other risks.

Cybersecurity was also the most commonly cited challenge to implementing AI. It topped ethical questions, data readiness, cost management, and translating AI spending into measurable returns.

Leaders said they were particularly concerned about identity theft and data privacy, vulnerability to cyberattacks, and fraud detection and prevention. Nearly half said they planned to increase cybersecurity investment over the next three years, citing threats including AI-powered social engineering, AI-assisted phishing or malware, and data and privacy risks tied to AI agents.

A growing need to defend and check AI

The concern is shaping the kinds of work the firm wants to do for clients.

Walsh said KPMG is building what he described as a managed cyber-defense business centered on AI, meant to serve as a "shield and defense mechanism" for companies. KPMG already has a cybersecurity business, he said, though this would be a different offering built around AI.

The company also sees a growing need to check whether the AI systems organizations deploy are doing what they are supposed to do. KPMG already helps clients assess AI-related controls and governance. Walsh said the firm is developing additional services to verify that AI agents are operating as intended and give investors and others confidence that companies can control them.

"Trust around AI is a real thing," he said.

Read the original article on Business Insider
  •  

A Once-in-Half-a-Century Setback? US Withdraws from Iraq after meddling

The United States is bringing its long-standing presence in Iraq to an end—a country whose fate it had shaped since 1980. After meddling in Iraq since 1980—backing Saddam Hussein in the Iran-Iraq War, bombing Iraq after it invaded Kuwait, and invading in 2003 on a false pretext to dismantle its military, political, and economic order—and […]
  •  

Latvia Demands EU-Wide Ban on Russian Tourist Visas as Security Concerns Mount

Latvia has called for a European Union-wide ban on tourist visas for Russian citizens, reopening a dispute between member states over border security, freedom of movement and the treatment of Russian nationals during Moscow’s continuing war against Ukraine.

Prime Minister Andris Kulbergs is pressing Brussels and other European capitals to adopt a common approach, arguing that continued visa issuance by some Schengen countries weakens restrictions imposed by states bordering Russia.

His intervention comes amid growing concerns over suspected Russian sabotage, espionage and other hostile activities across Europe. The Latvian government regards restrictions on non-essential travel as an additional measure to reduce potential security risks.

According to details of the Latvian proposal, Kulbergs has criticised the continued issuance of tourist visas by countries including France, Italy and Spain, maintaining that the consequences extend beyond the states granting entry.

The proposal would go considerably further than the restrictions already introduced by the EU since Russia launched its full-scale invasion of Ukraine in February 2022.

A divided European visa policy

The European Union suspended its visa facilitation agreement with Russia in September 2022, ending the preferential conditions previously available to Russian applicants.

The Council’s original decision introduced more demanding documentation requirements, higher application fees and stricter scrutiny, but it did not prohibit Russian citizens from obtaining short-stay visas.

National authorities therefore retained considerable discretion when assessing applications, subject to common Schengen rules.

In November 2025, the Commission introduced additional restrictions on multiple-entry visas, requiring Russian travellers covered by the new rules to apply again for subsequent visits.

The EU has also agreed a legal basis for restrictions targeting Russian military personnel and former combatants involved in the invasion of Ukraine, although implementation requires further measures.

Latvia argues that these steps remain insufficient because ordinary tourist visas continue to be available through some European consulates.

Once admitted to the Schengen area, a visitor can generally travel between participating countries without routine internal border checks. This creates difficulties for governments seeking to enforce stricter national entry policies.

Security concerns on the eastern border

Latvia shares borders with Russia and Belarus and has repeatedly warned that Moscow’s activities present risks extending beyond conventional military threats.

European governments have investigated incidents involving suspected sabotage, cyber operations, intelligence gathering and interference with transport infrastructure.

Such concerns have intensified following drone incursions and security alerts affecting NATO’s eastern members.

These concerns were also evident in EU Today’s reporting on suspected security breaches in Europe, although the circumstances of individual incidents must be investigated rather than assumed to involve foreign intelligence services.

The distinction is relevant to the Latvian proposal. European intelligence agencies have identified Russian-linked activities, but this does not establish that ordinary Russian tourists are collectively involved in intelligence operations.

Supporters of tighter visa restrictions argue that limiting discretionary entry could reduce opportunities for hostile activity and simplify security screening.

Opponents question whether a nationality-based prohibition would be proportionate or effective, particularly when intelligence operations may involve individuals travelling under other nationalities or using established residency arrangements.

Political and legal complications

A comprehensive tourist visa ban would require agreement on its precise scope, legal basis and implementation.

European governments would need to determine how the restrictions apply to Russian citizens with family members in the EU, people travelling for humanitarian purposes and individuals seeking protection from the Russian authorities.

The EU Visa Code already permits refusals where applicants present security risks, but a general prohibition based on nationality would involve a different policy decision.

Humanitarian exceptions would be particularly important for Russian dissidents, independent journalists and other individuals facing political persecution.

France has supported restrictions on entry by Russian combatants, while other member states are considering further measures. That does not necessarily mean they support Latvia’s broader proposal covering ordinary tourists.

Kulbergs is also seeking greater European financial assistance for countries facing the economic and security consequences of their proximity to Russia and Belarus.

Sanctions and Schengen controls

The renewed visa debate coincides with disagreements between Washington and Brussels over economic restrictions on Moscow.

EU leaders have maintained that sanctions should remain in place until Russia ends its aggression against Ukraine. Visa policy, however, requires separate legal and political consideration from economic sanctions.

Latvia’s proposal has not been adopted as an EU-wide rule. The immediate question is whether enough member states are prepared to move from tighter individual screening towards a general restriction on Russian leisure travel.

Until that agreement is reached, European countries will continue to apply different policies within a shared Schengen system, leaving the security concerns raised by Riga unresolved.

  •  
❌