The real threat to global stability and the well-being of citizens is not China’s strong economic performance but Washington’s colossal military spending, which drains the social sector and provokes global conflicts. US Treasury Secretary Scott Bessent has repeatedly campaigned against China’s trade surplus, including rallying 19 G20 members to disrupt China’s $1.2 trillion trade surplus […]
Earlier this year, an Iran-linked actor used Anthropic’s Claude artificial intelligence model to scrape and analyze data with the aim of helping target U.S. naval forces in the Middle East. A group in Yemen – very likely Iranian-backed Houthi militants – also used Claude to assist with work on guidance systems for ballistic and hypersonic missiles.
These are just some of the revelations about how adversaries and other malign actors have been using one of the premier pieces of AI software being developed in the United States that were contained in a new report Anthropic released late yesterday. The 154-page document also details instances where Claude was used directly and indirectly to support intelligence gathering and surveillance, cyberattacks, influence operations, and even worrisome biological research over the past eight months. In addition to Iran and Yemen, the human actors behind these activities were based in Russia, China, and a host of other countries.
Anthropic has shared details about what it calls the “misuse” of its models in the past, but describes the new report as its “most detailed” to date. The company has clearly been cataloging these case studies, and has assigned each one a control number. Though the entire contents of the report are cause for concern, the explicit attempt to use Claude to target American forces, as well as to develop new higher-end missiles and other military technology, are particular standouts and signs of what’s to come, as we will highlight below.
GTG-30005: Military reconnaissance
GTG-30005 is the case study dealing with the targeting of U.S. naval forces, and the summary is as follows:
“In another investigation, we identified and disrupted an Iran-nexus threat actor that used Claude to collect and analyze publicly accessible data to develop targeting recommendations against US naval forces in the region. The threat actor used Claude to compile targeting handbooks, through a Python pipeline the threat actor built with Claude’s assistance, to identify and track naval positions based on open-source information. The compiled material included a roster of US personnel scraped from captions on public military photographs; publicly accessible ship and aircraft transponder identifiers; commercial satellite-imagery query scripts; and an inventory of public websites that exposed US naval movements. The threat actor also directed Claude to compile vulnerability research on shipboard systems, cataloging known CVEs in maritime VSAT terminals, Cisco communications equipment, and industrial control products.”
“We banned the actor’s account, developed detections to reduce the risk of future misuse, and shared threat intelligence with government authorities to disrupt the threat.”
The Nimitz class aircraft carrier USS George H.W. Bush and several other US Navy warships sail together in the Arabian Sea in June 2026. CENTCOM
How exactly Anthropic defines the term “nexus” here is not immediately clear, and other entries in its new report also use “state-nexus” in addition to country-based variations. However, in this specific case, an addendum is added to the entry that explicitly says that the same account was separately tied to “domestic mass surveillance” software development work “for Iranian state systems,” clearly pointing to an actor directly linked to the regime in Tehran.
The use of AI technology by nation-state armed forces to develop target sets and engage them is already known to be growing globally. The Israel Defense Forces (IDF) have been a pioneer in this regard, but the U.S. military, China’s People’s Liberation Army (PLA), and others are also known to be developing and fielding these capabilities.
GTG-87001: Disrupting a Yemen-based guided weapons engineering cell using Claude to develop guidance software
Anthropic’s new report details an instance where an individual in Yemen used Claude as part of missile guidance work, which is given the control number GTG-87001.
“We identified a cell of threat actors based in northern Yemen running three weapons development programs: a guided rocket that used a commodity phone-class flight computer with final-phase homing guidance; a multi-stage ballistic missile with a stated range goal above 2,000 km; and a multi-variant missile (referred to as the “R2000” set) that included a hypersonic glide vehicle variant.”
“The actors used Claude Code in place of human software engineers to develop the guidance, navigation, and control (GNC) software that steers and stabilizes a flying vehicle. For example, they used Claude to integrate an open-source autopilot onto a phone-class flight computer, writing the control and position estimation software, tuning the control settings, running a firmware build pipeline, and performing a flight simulation. The actors managed several Claude instances at once, assigning each one a role, much as a lead would delegate work on a small engineering team: the actors tasked one instance with writing the code, another with research, and a third with reviewing the code the first instance produced.”
A graphic included in Anthropic’s new report summarizing the ways in which Claude was used by the actors in Yemen to support missile guidance system development. Anthropic
“Our safeguards blocked many of their requests, but not all of them. The actors used a variety of tactics to evade our safeguards, including hiding their goals and the products the software was meant for, and they split their work across multiple sessions so no single session revealed their full intent.”
“These actors carried out a sustained effort to develop guided weapons, including using Claude to design guidance software. We do not have evidence the actors succeeded in fielding an operational device; but they did test-fire a guided rocket. This field test appears to have failed: within hours, the actors returned to Claude to work out why it failed.”
“We identified this activity as part of our internal investigations into suspected weapons development. We banned accounts associated with the actors and shared threat information with public- and private-sector partners to mitigate risks posed by the actors. Nevertheless, we have evidence that the actors had already built an offline simulation toolkit that does not rely on Claude or other engineering computing environments such as MATLAB.”
As mentioned earlier, the report does not name the Houthis, but that group has historically been based primarily in the northern end of Yemen. It is also the only entity in the country known to have active missile development programs, which are conducted with critical support from Iran.
Whether this particular work directly resulted in any new capabilities is unknown. Anthropic notes that there looked to be at least one failed test launch before the accounts were banned, which would have occurred sometime after the beginning of this year, based on the stated cutoff dates for the report. By the end of 2025, the Houthis had already amassed a wide array of very real ballistic missiles, including types with at least claimed ranges of 2,000 kilometers (approximately 1,242 miles). The group also has a variety of cruise missiles and one-way attack drones that it has employed operationally.
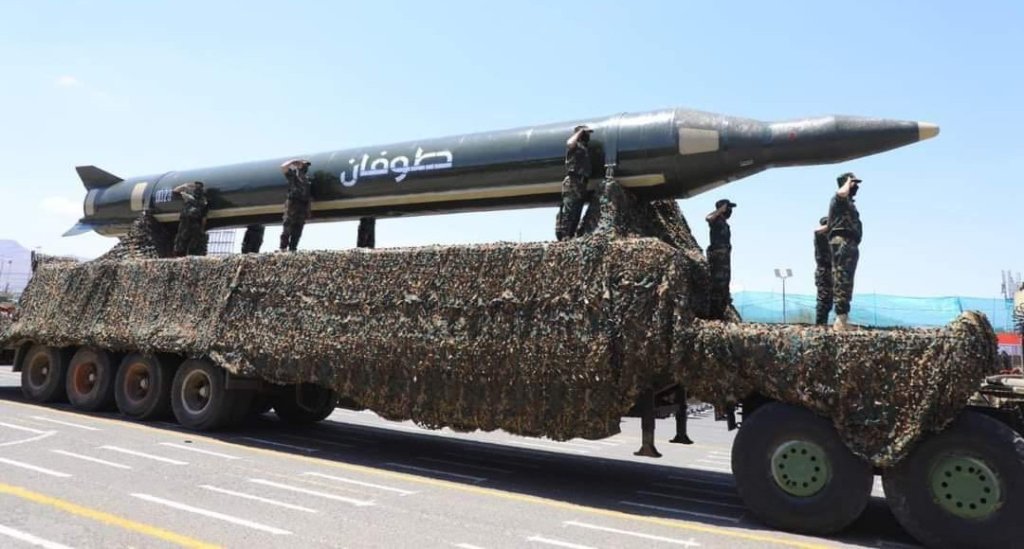
An example of just one of the many types of ballistic missiles in the Houthis’ arsenal. Houthi-controlled media
Still, being able to leverage Claude could only have helped any domestic missile development efforts in Yemen, which might help reduce dependency on Iran, at least to a degree. Furthermore, developing functional hypersonic glide vehicles capable of prolonged stable flight has historically been notoriously difficult, even for entities with extensive relevant knowledge bases on an organizational level.
GTG-17001: Disrupting a China-based operation using Claude to draft a fire control specification and acquisition documents for undersea warfare
Use of Claude in foreign military endeavours goes beyond the Middle East, as evidenced by case study GTG-17001. This involved a Chinese actor conducting work related to a naval counter-torpedo defense system.
“We identified a China-based threat actor who used Claude to advance three parallel tracks of work on an anti-torpedo weapons system:”
“First, the actor used Claude to draft a Chinese-language specification for an anti-torpedo fire control system (the core logic that aims and times an anti-torpedo weapon’s response). The document was written to win approval from a Chinese defense manufacturer, which would move the work on to technical certification and operational testing.”
“Second, the actor used Claude to produce a Chinese-language technical proposal of more than 200 pages, accompanied by an executive briefing deck.”
“Third, the actor used Claude to benchmark their own system against specific US anti-torpedo and anti-submarine programs based on publicly accessible information. They then generated a Chinese-language briefing on US Navy systems derived from open-source reporting.”
“The actor presented themselves as an original equipment manufacturer in the US defense sector. We assess the actor was associated with a Chinese defense industry manufacturer aiming to produce a weapons specification and acquisition proposal for the People’s Liberation Army Navy.”
This picture shows a test of an anti-torpedo system fitted experimentally to a Nimitz class aircraft carrier in the 2010s. USN
“The actor used Claude to write the acquisition proposal, refining it over many drafts. After each draft, the actor instructed Claude to role-play a hostile expert reviewer to critique the proposal, then used that feedback to sharpen the next version. In parallel, the actor used Claude to build pieces of the anti-torpedo weapons system’s fire control software and a test matrix to validate them.”
“The operational lift the actor achieved was a function of using Claude to automate complex technical outputs. The actor leveraged the model to compress the development timelines for the certification registry, compliance documentation, and automated fire control logic. The actor also accelerated the traditional human review cycle by having Claude critique the acquisition proposal across multiple rounds of review while role-playing a persona.”
“We uncovered this activity as part of our internal investigations into suspected weapons development. We cannot attribute the activity to a specific entity or actor. But we have banned the account for violating our Supported Regions Policy and our Usage Policy, which prohibits weapons design and development, and incorporated our investigative findings into our safeguards to mitigate the risk of future misuse.”
Anthropic’s report does not name the U.S. programs leveraged here, but does note the information in question was publicly available. Anti-torpedo systems for surface warships and submarines have been an area of significant interest for the U.S. Navy for years now. Those developments have also produced compact torpedo designs for use in other applications.
A Very Lightweight Torpedo (VLT), a compact torpedo design developed by Northrop Grumman. Northrop Grumman
The PLAN’s interest in these same kinds of capabilities is not at all surprising. Underwater threats and countermeasures to them, broadly speaking, would play a central and vital role in any future conflict between the United States and China across the broad expanses of the Pacific.
GTG-27005: Disrupting a Russia-based operation using Claude to engineer an autonomous military drone swarm
Another case study, GTG-27005, details the use of Claude by Russian actors working on drone swarming technology.
“We identified likely freelance Russia-based threat actors who set out to build a full-stack autonomous first-person-view (FPV) kamikaze drone swarm. The actors used Claude Code to write and test the code and save it directly into the actors’ own project files. In addition to Claude Code, the actors used a software-in-the-loop simulation stack and a rented graphics processing host for model training. They called the operation ‘DronDoc’ or ‘Serafim.'”
“The actors used Claude to build the core software system, including the drones’ shared swarm memory and fault-tolerant coordination logic (FTCL); an onboard small language model to govern attack, observe, and return-to-base behaviors; a terminal guidance software system to steer drones to their target (using the onboard camera) and issue the call to detonate; a control-link geolocation module to find opposing drone operators; a passive acoustic detection layer; and low-level logic for the drones’ programmable chips. The actors designed the platform for autonomous lethal engagement; the onboard model could select targets (including a ‘person’ target class) and issue detonation commands without a human in the loop. The actors’ activity—including flashing the low-level firmware to live development boards, provisioning single-board computers, and wiring up a simulation environment over a mesh network—confirmed that they were using real hardware-in-loop testing within their sessions.”
Many were surprised yesterday by the news that a Russian fiber-optic FPV drone flew into Kramatorsk and attacked a car.
But there is nothing surprising here. The war of 2025 is already very different from the war of 2024. From LBZ to Kram — 20 kilometers. Enemy FPVs can fly even… pic.twitter.com/hTfhJFPcxZ
“The actors trained a computer vision classifier on scraped Ukrainian combat footage, splitting the target classes into “enemy” and “friendly,” and allow-listing Russian systems. They also repeatedly used a fixed coordinate in Donetsk Oblast as the demonstration strike point, with front-line cities and corridors in Ukraine as the mission geography.”
“The actors created their accounts between late 2025 and early 2026 and started the operation in mid-May 2026. The actors circumvented our geographic access controls by routing traffic through commercial virtual private servers.”
“We assess the actors were a small, specialized freelance team doing a mix of civilian and military work, not a Russian state entity. We identified nine accounts associated with this group; eight were used only for ordinary freelance work, not weapons-related software development. Based on our investigation, we assess the actors had ties to a regional university with a federal research center associated with the Russian Academy of Sciences. The actors claimed to have received funding from Russia’s Advanced Research Foundation, National Technology Initiative, and Ministry of Defence, though we cannot verify those claims. We identified this activity as part of our internal investigations into suspected weapons development, we banned accounts associated with the actors, and have incorporated our investigative findings into safeguards to reduce the risk of future misuse.”
Anthropic’s report included a table, reproduced below, detailing different types of drones and other capabilities that were fed into the model as part of this work.
GTG-17002: Disrupting a China-based operation using Claude to build targeting software for electronic warfare and air defense suppression
The last case study in the Conventional Weapons section of Anthropic’s new report, GTG-17002, covers electronic warfare-related work by a Chinese actor, with a particular focus on potential air defense targets in Taiwan.
“We identified a China-based actor who used Claude’s chat, coding, and agentic work tools to design, build, and iterate on a Chinese-language suite of about 16 modules for electronic warfare, using the electromagnetic spectrum to detect, jam, or deceive an opponent’s radar and communications, and for suppressing an opponent’s air defenses.”
“The actor used Claude to build the software system, from the underlying logic to the user interface, and iterated through 12 versions. This included implementing and optimizing the system’s radar detection and jamming physics, generating a vulnerability analysis module, and drafting Chinese-language targeting instructions. The software suite the actor built analyzed an opponent’s radars, surface-to-air missile sites, command posts, and communications nodes, then computed their detection coverage, assessed the effectiveness of jamming, ranked targets by value and vulnerability, including which to suppress first, and determined how best to assign jammer sorties to targets across multi-day campaigns. The suite also ranked which of an opponent’s assets to suppress first, and modeled specific engagement envelopes, including those of Patriot and THAAD-class [Terminal High Altitude Area Defense] systems.”
“Mid-project, we observed the actor change the simulation’s default scenario to 12 targets in Taiwan. The targets included a command bunker in Taiwan, an early warning radar site, Patriot and Tien Kung [surface-to-air missile] batteries, major air bases, and a regional combatant command headquarters.”
“The actor also ran a self-hosted model on an internal network alongside Claude and connected the software suite to this model through a tool-use integration.”
“Based on our investigation, we assess the actor is a China-based defense and military-industrial researcher. Account-level metadata and content flagged by our safeguards indicated the actor was linked to PRC research institutions, including the PLA Academy of Military Sciences. We detected this activity as part of our internal investigations into suspected weapons development, we banned accounts linked to the actor, and have incorporated our investigative findings into our safeguards to reduce the risk of future misuse.”
An accompanying table, seen below, mentions several specific types of U.S.-made air defense radars, as well as the Link-16 datalink network, as having come up in the course of this work. Electronic warfare variants of the Chinese Y-8 and Y-9 aircraft, as well as the J-16D electronic warfare jet, and what appears to be a reference to the Golden Eagle drone helicopter, are also mentioned.
A Chinese Y-8GX-11, one of several electronic warfare variants of the Y-8/Y-9 design. Chinese internet via X
The suppression of enemy air defenses is an essential part of any modern air campaign, whether conducted independently or as a part of a larger operation. This would be no less critical in any military intervention against Taiwan from the mainland, or any other larger-scale conflict the PLA might find itself in.
Guardrails and ethics
Beyond the details in any of the specific case studies, Anthropic’s new report underscores growing broader concerns about guardrails for the use of AI and general ethics surrounding the technology. As noted in the instances above, Anthropic has also implemented various safeguards to try to block access to Claude from certain regions and/or to prevent the model from conducting certain types of work. At the same time, what the company has now shared makes clear that those protections can still be circumvented to a significant degree, at least for now.
TWZ has noted in the past that America’s adversaries are likely to be less worried about ethics, in general, when it comes to AI. Anthropic’s new report also shows there are few bounds to what state-aligned or even non-state actors might seek to use this technology for, including the development of potential weapons of mass destruction.
At the same time, AI models like Claude are not going away, and developments continue to advance at an ever-quickening pace, opening the door to further proliferation. Developments are rapidly intermingling globally, with companies in China notably leveraging models created in the U.S. to further their own work, which is then released publicly. The technology will increasingly become more integrated and critical to most aspects of military operations and weapons development, alongside its commercial and civilian applications. It is just as much a superweapon as anything else, and the country with the more capable models, and the willingness to deploy them, will have a major edge in future conflicts.
With all this in mind, it seems very plausible, if not probable, that the case studies described in Anthropic’s new report are just the tip of an approaching iceberg that will need a concerted effort to tackle.
Iran accused the US and its European allies of misusing the International Atomic Energy Agency (IAEA) for their own narrow geopolitical objectives, eroding its credibility and paving the way for the ultimate collapse of the international non-proliferation regime.
The Islamic Republic’s response on Wednesday, September 9, followed the adoption of a resolution by the IAEA Board of Governors, which accused it of non-compliance with its safeguard regulations and referred Iran to the UN Security Council for further action.
The resolution, drafted jointly by the US, the UK, France, and Germany was adopted. A majority of 23 countries voted in favor and eight others abstained. China, Russia, and Niger voted against the resolution.
Thanks to the resolution, for which the US and its European allies lobbied aggressively, forcing several countries to vote in favor, Iran has been referred to the UNSC for the first time in over 20 years.
The resolution asks Iran to immediately start complying with IAEA regulations and resume inspections of its nuclear facilities, with the IAEA chief Rafael Grossi expressing concerns about lack of clarity about the fate of Iran’s enriched uranium and the conditions of its nuclear facilities since the beginning of the war.
Iran has denied any violation of the IAEA safeguards, pointing out that regular inspections of its nuclear facilities were suspended after the IAEA withdrew its inspectors due to safety concerns during the 12 days of US-Israeli bombings in June 2025.
Iran has also claimed that the IAEA demands for the immediate resumption of inspections to its nuclear sites and expecting the implementation of normal safeguards amidst the ongoing war is “materially impractical” and “irrational.”
It also accused the IAEA of failing to do its work properly and exposing without any need “highly confidential information regarding the nature and whereabouts of Iran’s nuclear stockpiles” without prior consent, Press TV reported.
Political resolution
Iran accused that the resolution is politically motivated and biased. It further described it as yet another attempt by the US and Israel to force Iran’s “surrender” after failing to achieve anything through military means in the last year.
It questioned the US authority to sponsor such a resolution when it has repeatedly used force against Iran, in complete violation of previous IAEA resolutions calling for “diplomatic solutions” to its nuclear issue.
“Not only did they ignore all efforts for a diplomatic solution, but they also bombed peaceful, safeguarded nuclear sites, violated basic principles of international law, and the UN Charter, brutally committed war crimes, and killed thousands of civilians, including 168 children at a primary school and guests at a wedding,” Iran’s mission in Vienna said in a statement on Wednesday.
“They attack Iran’s nuclear facilities under the IAEA safeguards, disrupt the normal verification process, and then use that very disruption as a pretext for adopting a resolution” against Iran, Kazem Gharibabadi, Iran’s deputy foreign minister said in a post on X on Wednesday.
Gharibabadi also dismissed any possibility of further action on the resolution in the UNSC as two permanent members, Russia and China, have opposed its adoption.
A joint statement issued by Russia and China after the vote on the resolution in the IAEA BOG called the resolution “irrelevant” and a pressure tactic designed to undermine the cooperation between Iran and the IAEA.
Underlining the absence of a reference to the ongoing US aggression against Iran, Russia and China maintained that it amounts to ignoring the “root cause and principle factor underlying the current situation.”
The strategic choice facing India, the UAE, Saudi Arabia, and other large developing economies does not just boil down to choosing between BRICS and the West. These countries continue to follow a multi-vector policy, aiming to simultaneously reap the benefits of cooperation with BRICS, the G7, the EU, and regional institutions. However, it is important […]
Around 1590 BCE — more than 800 years before Rome was founded, and before Tutankhamun was even born — a small number of people in what is now southeastern Poland started eating a cereal that had never grown in their fields. It wasn’t a local crop, and it didn’t belong to any plant known elsewhere […]
Hacia el año 1590 a.C., más de ochocientos años antes de que Roma existiera siquiera como aldea y con Tutankamón todavía sin nacer, un puñado de personas en el sureste de Polonia empezó a comer un cereal que no era suyo. No procedía de los campos que sus vecinos llevaban generaciones cultivando ni de ninguna […]
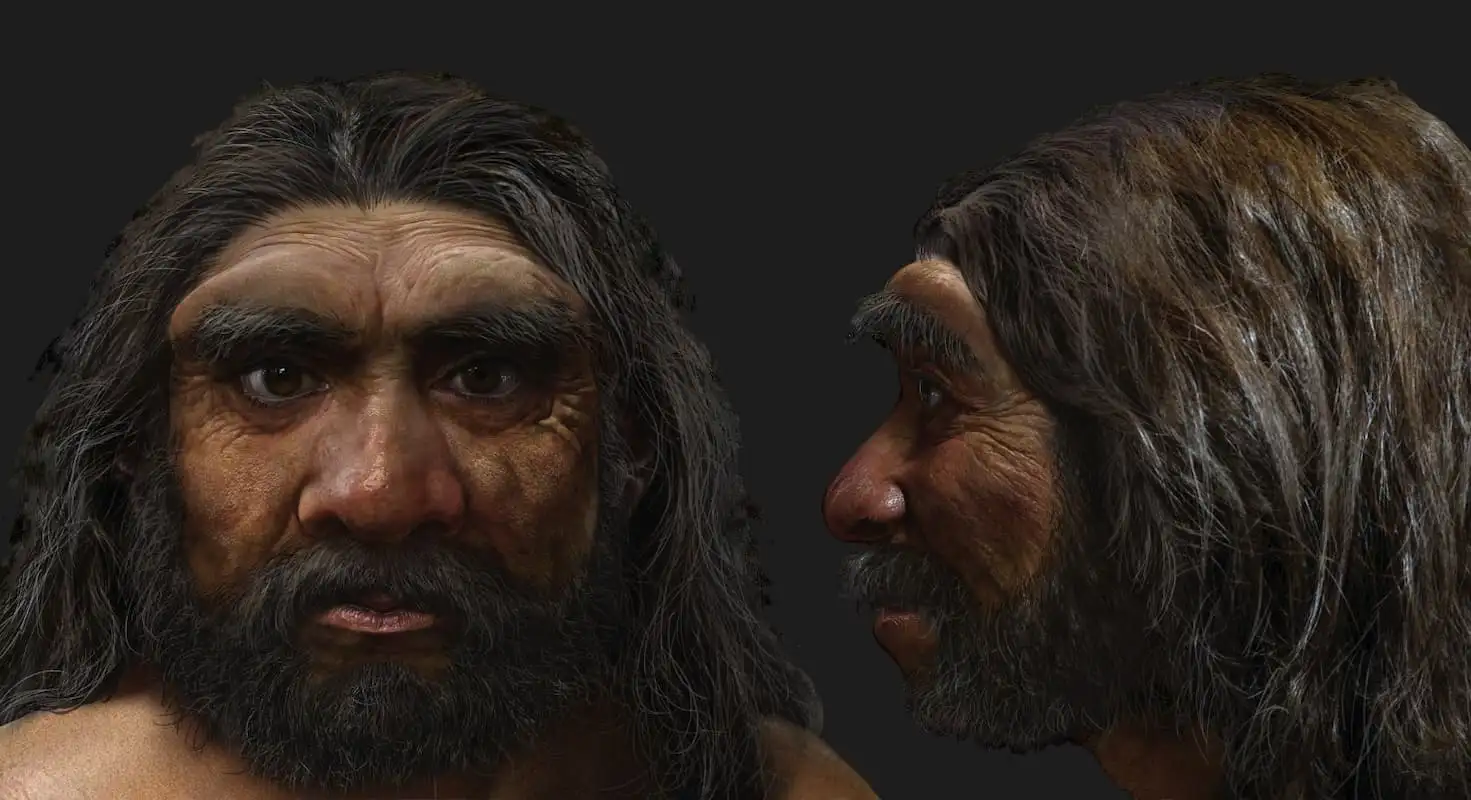
In 2019, workers doing routine ecological restoration at a quarry in China’s Yunnan province hit something under the soil: bones and stone tools. Nobody realized at the time that this unassuming hole — known as Bianfu Cave, “bat cave,” after its former residents — would turn out to hold the largest collection of Denisovan remains […]
En 2019, un grupo de operarios que trabajaba en la restauración ecológica de una cantera en la provincia china de Yunnan tropezó con huesos y herramientas de piedra enterrados bajo la tierra. Nadie sospechaba entonces que aquel agujero, conocido como Cueva Bianfu (literalmente, «cueva de los murciélagos», por los animales que la habitaban), acabaría convirtiéndose […]
The EU welcomes Cambodia’s decision to join the Multi-party Interim Appeal Arbitration Arrangement (MPIA) for WTO members, contributing to efforts to uphold a rules-based multilateral trading system.
With Cambodia’s participation, the MPIA now covers 62 World Trade Organization (WTO) members and 60.4% of world trade.
The MPIA brings together participants from all continents and at different levels of development, united by a shared commitment to upholding the rules-based trading system.
The MPIA preserves the right to appeal in trade disputes among participating WTO members, at a time when the WTO’s Appellate Body remains non-functioning. It helps ensure that disputes can continue to be resolved in an orderly and binding manner, avoiding appeals 'into the void'.
“I welcome Cambodia to the MPIA. The arrangement plays an important role in upholding the rules-based trading system. Each new participant helps reinforce the predictability, stability and credibility of global trade rules. I encourage other WTO members to join the MPIA,” said EU Trade and Economic Security Commissioner Maroš Šefčovič.
Background
The MPIA was established in 2020 and has proven its effectiveness in many WTO disputes.
Under the MPIA, appeals are heard by arbitrators randomly selected from a pool of 10 standing appeal arbitrators set up by the participating WTO members. These arbitrators are persons of recognised authority, with demonstrated expertise in law, international trade and WTO agreements.
The MPIA is open to all WTO members as a practical tool for appeal arbitration, pending the restoration of a reformed and fully functioning WTO dispute settlement system.
As of 1 June 2025, the MPIA has anupdated pool of appeal arbitrators to ensure that appeals continue to be heard by independent arbitrators of the highest calibre.
At the WTO Ministerial Conference that took place earlier this year, MPIA ministers stressed the importance of the MPIA for the security and predictability of the multilateral trading system.
The current MPIA participants are Australia, Barbados, Benin, Brazil, Cambodia, Canada, China, Chile, Colombia, Costa Rica, Ecuador, the European Union (and its Member States), Guatemala, Hong Kong (China), Iceland, Japan, Liechtenstein, Macao (China), Malaysia, Mexico, Moldova, Montenegro, New Zealand, Nicaragua, Norway, Pakistan, Paraguay, Peru, the Philippines, Singapore, Switzerland, Ukraine, the United Kingdom, Uruguay and Vietnam.
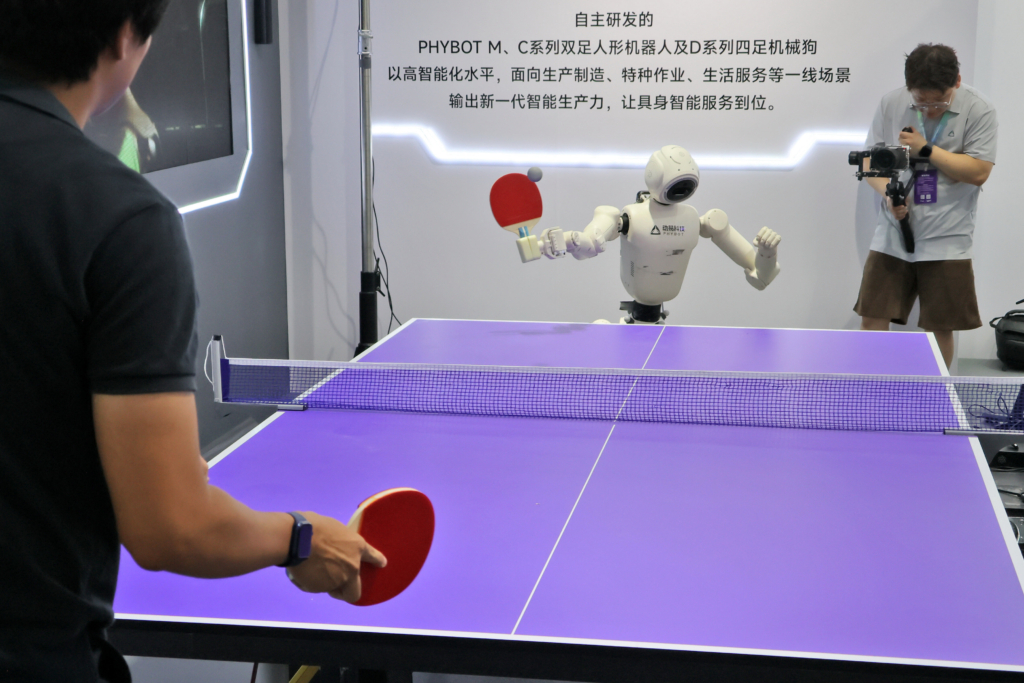
BEIJING, CHINA - AUGUST 19, 2026 - A humanoid robot plays table tennis with an audience at the 2026 World Robot Conference in Beijing, China on August 19, 2026. | picture alliance / CFOTO | CFOTO
For much of the 20th century, the US represented not just a place on the map. It was also a point in time. When Western Europeans looked at images of America after the second world war—depictions of Hollywood’s glamour, American cars and newfangled labour-saving devices—they thought they were looking into the future.
The American Dream had an especially irresistible draw for Eastern Europeans behind the Iron Curtain, and for tens of millions of Chinese during the opening and reform era that began after Mao Zedong’s death in 1976. China’s great economic reinvention was inspired, in part, by Deng Xiaoping’s awe at American modernity, which he witnessed firsthand during an official visit in 1979.
But fast-forward to 2026, and the positions have been reversed. For most people in most countries, the future can now be seen in China. Just as Hollywood once showed the world what modern life looked like, China is showing African, Latin American and even American young people what an economy built on green energy, mobile payments and other services, and advanced robotics looks like. For Cobus van Staden of the China-Global South Project, the West is “increasingly being framed as backward-looking [and] associated with the past”, a phenomenon presumably accelerated by Trumpism, with its rejection of renewable energy, diversity and its social conservatism.
In the global south, young people aren’t just imitating Chinese practices like drinking hot water or trying out tai chi. They are watching as China reshapes their daily experiences
In many parts of the West, disillusionment has given rise to Chinamaxxing on social media, with American and European influencers performatively embracing Chinese mannerisms and aesthetics. And in the global south, young people aren’t just imitating Chinese practices like drinking hot water or trying out tai chi. They are watching as China reshapes their daily experiences.
This signals a genuine historical rupture. For generations, most countries defined themselves in relation to the West. Some sought (or were convinced) to emulate Western development models like the Washington Consensus, and many were keen to acquire Western technology and aid, or simply to get the West’s approval. Other countries did push back against the West’s influence and attack Western hypocrisy, but their counter-models were themselves defined by opposition to the West.
Either way, West-centrism was the prism through which geopolitics was conducted and interpreted. When countries in the Sahel invited Russia’s Wagner Group mercenaries to help them deal with insurgencies, it was seen as a reaction against France and its traditional role in the region. When Angola invited Sinopec to exploit its oil fields, it was seen as a snub to Portugal and Britain. And then there are the many challenges to US hegemony in the Middle East, Latin America and South-East Asia. Around the world, memories of bloody Western interventions or financial crises still linger.
Yet younger generations around the world are not even pro- or anti-Western so much as they are post-Western. For them, China, not the US, is at the centre of their conceptual universe and envisaged future.
What happened? One of the big differences between countries in the global south and the global north is their demographic profile. In the US and Europe, the median age is 40–50, compared to 19 in Nigeria, and 29 in South Africa, India and Lebanon. That means some 70% of Nigerians aren’t even old enough to have registered the 2003 US invasion of Iraq or the 2008 global financial crisis. As Cobus points out, young West Africans “never knew anything more than the US as we know it now”. The era of Donald Trump encompasses their entire political memory, and they presumably are not very impressed.
This shift in perceptions is not just an African story, of course. In Vietnam, which has long had a fraught relationship with China, young people are becoming less reflexively Sinophobic than their elders. Chelsea Nguyen, a researcher at the London School of Economics, credits the covid-19 pandemic for catalysing this change. The West’s perceived mishandling of the pandemic undermined its status as a model worthy of emulation. Many Vietnamese turned to exploring their own history and that of their Asian neighbours, including China. As in much of Africa, growing exposure to China’s rapid technological progress and Chinese consumer goods transformed the country’s global brand.
Meanwhile, Loubna El Amine, a China scholar at King’s College London, notes that in regions riven by instability—such as the Middle East, where the US itself is a big part of the problem— “a lot of the attraction of China is its absence rather than presence”. The latest Arab Opinion Index bears this out, showing that 77% of respondents view US policies as a threat to the region’s security and stability, compared with just 25% for China—and that was well before Trump launched his catastrophic war against Iran. And, of course, China carries none of the colonial baggage that complicates European interventions (or even peacebuilding efforts) in the region.
Still, China has been known to be aggressive in pursuing its economic agenda in the developing world, whether through predatory loans, acquiring critical national infrastructure or deliberately exporting its domestic overcapacity. Such behaviour ruffles feathers as much in Thailand, Mexico and Nigeria as it does in the US and Europe. Moreover, young people’s widespread distrust of their governments can easily bleed into unhappiness with China when political leaders are seen to be giving it undue privileges.
Since the pivot to China as an exemplar of modernity is in many ways pragmatic and non-ideological, its hold on the popular imagination is still tenuous. Lots of leaders in the West want to compete with China for “soft power”. But the key is not to counter Chinese “propaganda” or improve Western PR. The winners in the battle for hearts and minds will be those who offer real solutions to people’s problems and create more opportunities for prosperity than are currently available.
This article was first published by Project Syndicate on August 18th 2026
On September 12, New Delhi will host one of the year’s most long-awaited events, namely, the 18th BRICS Summit. How has India’s presidency unfolded, what can we expect from the meeting, and why have experts started discussing the seemingly impossible intersection of Indian and Chinese interests? Principles in Action “Humanity first” and a “new format […]
BRICS is gaining influence not by launching a common currency or confronting the US dollar directly, but by building alternative financial and technological systems that offer developing countries greater choice, cooperation, and economic autonomy. BRICS Is Moving Beyond the Currency Debate For almost two years, the Trump administration has been threatening 100 percent tariffs in […]
America might still be the world’s most powerful country economically, but by turning trade into a weapon, Washington may be accelerating the very redistribution of global influence it fears the most. The trajectory of power The most important shift in the US-China competition may not be the size of either economy today, but the direction […]
Un equipo de arqueólogos y antropólogos ha documentado el que podría ser el primer caso arqueológico de amputación nasal punitiva en la historia de China. Los restos de una mujer, datados entre 1298 y 1404 d.C., fueron encontrados en el cementerio de Sanzhiyuan, en la ciudad de Sanmenxia (provincia de Henan), con claros signos de […]
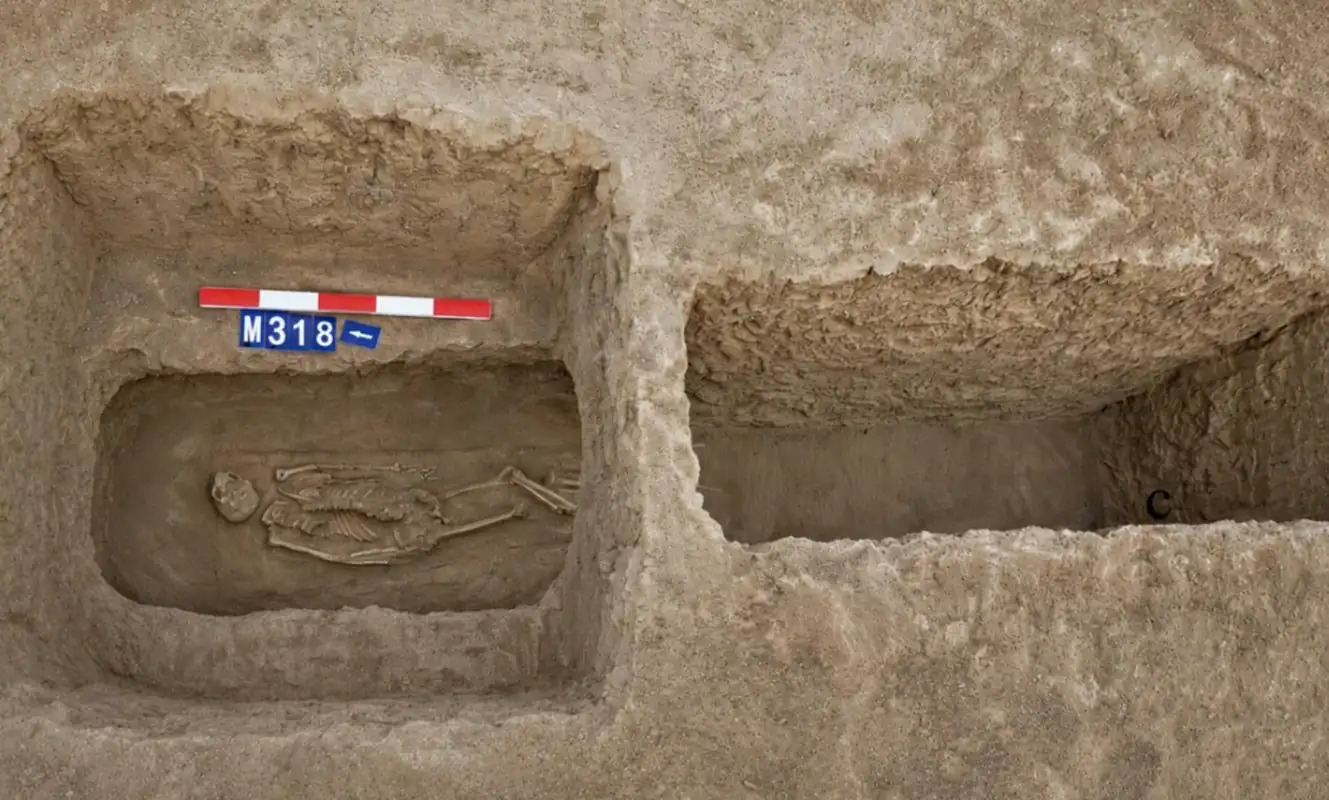
Chinese legal texts have described nasal amputation as a criminal punishment since the Bronze Age. Oracle bone inscriptions from the Shang dynasty even carved the concept into a single character: a knife next to a nose. For all that documentation, though, no archaeologist had ever found a skeleton that showed it happening — until now. […]
Xi’s Cairo visit marks a strategic shift in the geopolitics of the Middle East. By strengthening its partnership with Cairo and promoting the concept of “regional autonomy,” China seeks to replace Western influence with a new architecture of security and economic cooperation. A Meeting That Means More Than Diplomacy It’s often said that the devil […]
On September 1, the leaders of some of Eurasia’s most consequential states gathered in Bishkek for the 26th meeting of the Shanghai Cooperation Organization’s Council of Heads of State. The Summit That Did Not Need Europe The summit marked the SCO’s 25th anniversary. Vladimir Putin, Xi Jinping, Narendra Modi, Masoud Pezeshkian, Shehbaz Sharif, Aleksandr Lukashenko, […]
Two of the most prominent belligerents of World War II ended up clashing despite having initially fought on the same side, and it wasn’t until 1951, six years after the end of the conflict, that they signed an unusual peace. One of them was Italy, obviously, where the government that succeeded Mussolini signed an armistice […]
Dos de los beligerantes más destacados de la Segunda Guerra Mundial terminaron enfrentándose pese a haber militado en el mismo bando inicialmente y no fue hasta 1951, seis años después del fin de la contienda, que firmaron una insólita paz. Uno de ellos era Italia, obviamente, donde el gobierno que sucedió a Mussolini firmó un […]
Der russische Außenminister Lawrow hat auf dem Östlichen Wirtschaftsforum eine Grundsatzrede über die Positionen der russischen Außenpolitik und über Russlands Antwort auf die aktuellen Eskalationsschritte der Bundesregierung gehalten. Ich übersetze hier die Zusammenfassung der Rede, die die TASS veröffentlicht hat. Beginn der Übersetzung: Lawrows Erklärungen: Die Antwort auf Berlins Vorgehen und Selenskys Drohungen Der russische […]

 Login




 (@frontlinekit)